[GAME THEORY] The Help Desk Is Becoming the New Intrusion Broker
Vishing works because urgency can become SaaS authority. Break the trust transaction without breaking support.
Vishing works because urgency can become SaaS authority. Break the trust transaction without breaking support.
“Blockchain ransomware” is the easy headline. The harder operational problem is extortion workflow survivability.
AlphaHunt examines how ransomware-as-a-service turns familiar enterprise weaknesses into repeatable extortion inputs—and why recovery maturity changes the attacker’s continuation game only after access. The full analysis separates observed behavior from assessed motive, maps operator, affiliate, broker, victim, government, and insurer incentives, and gives defenders a practical way to pressure the edge-to-recovery path before encryption.
The next software supply-chain breach may not begin with malicious code. It may begin with a legitimate connector carrying a stolen OAuth token and the permissions customers already granted it
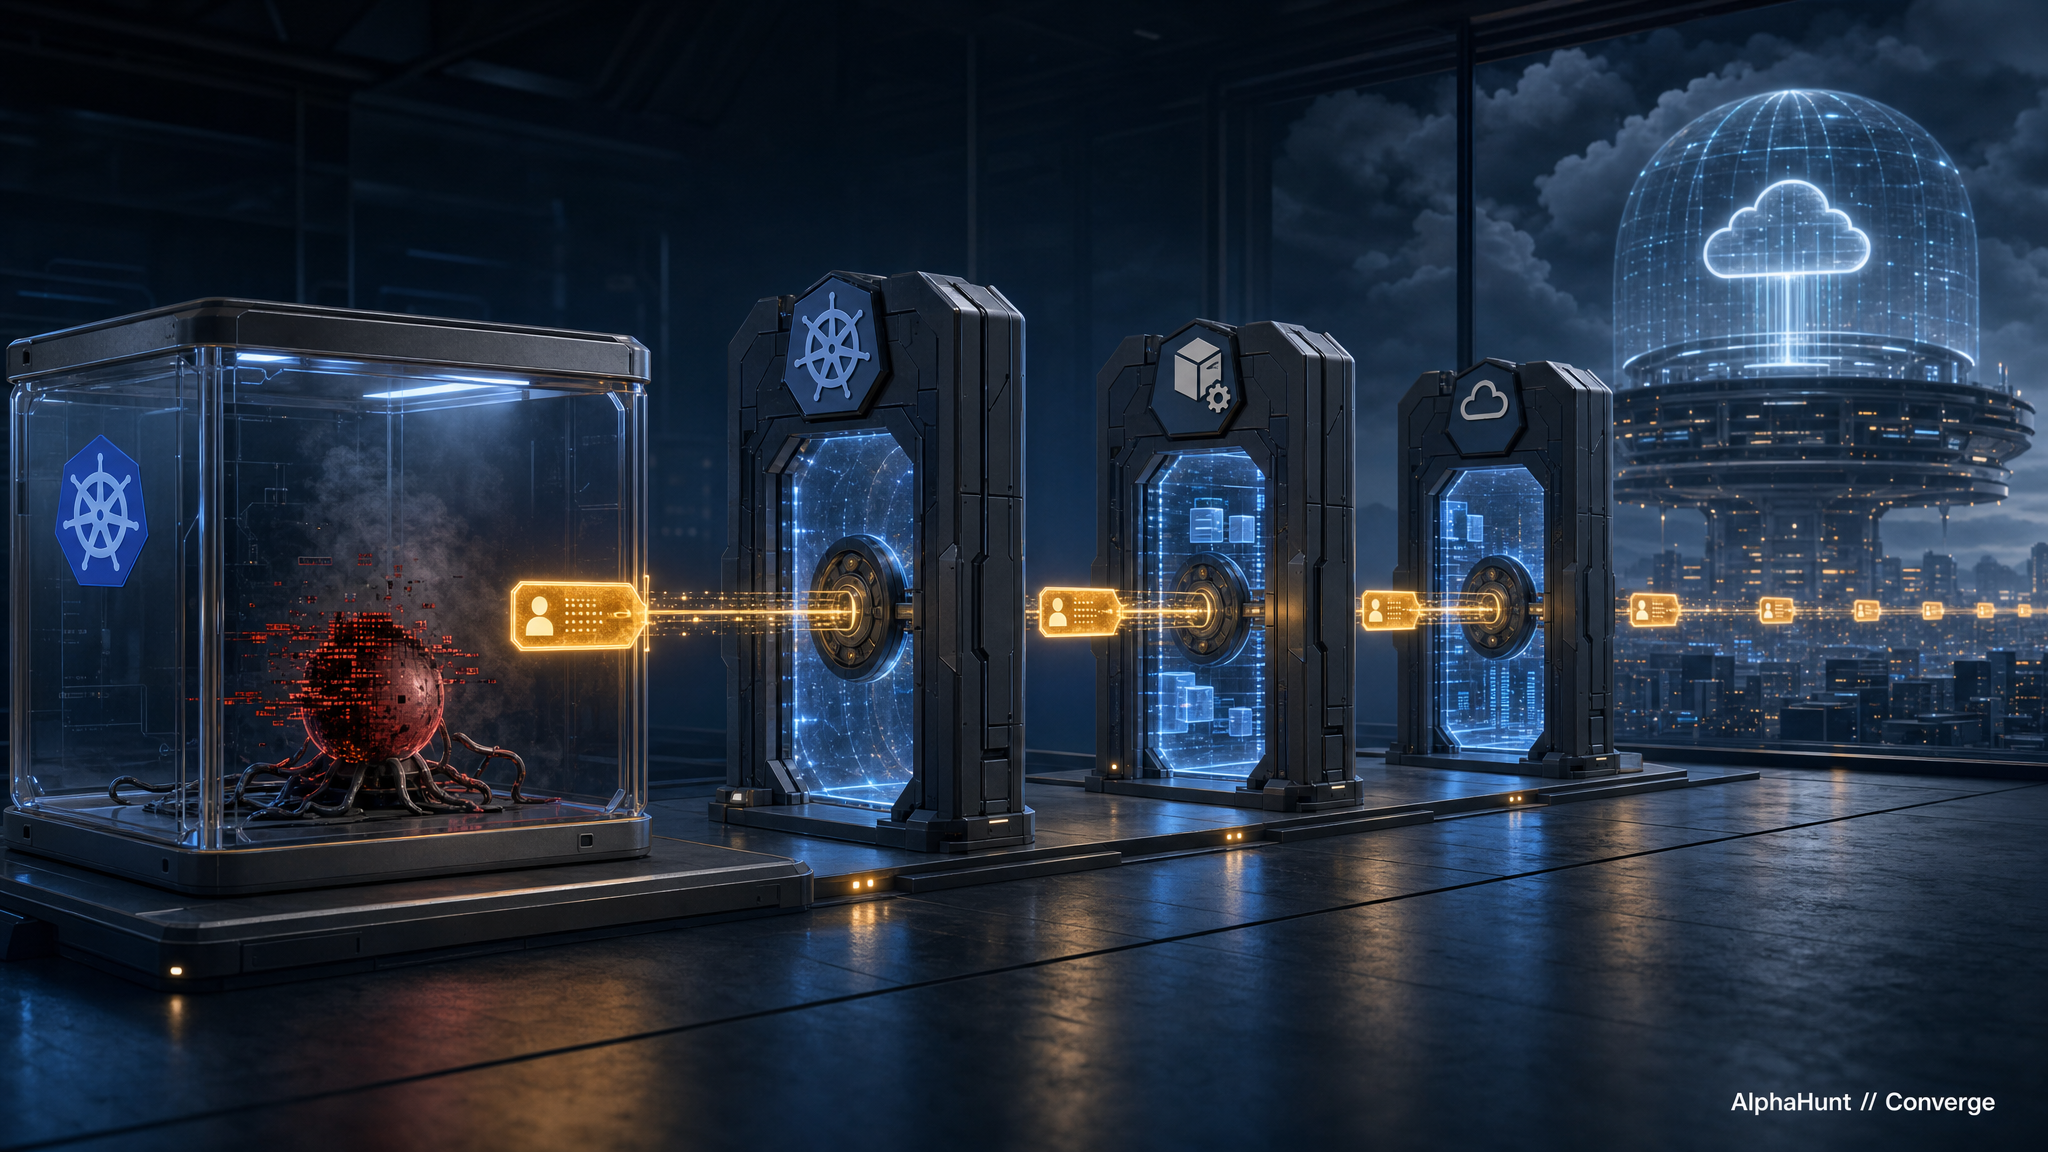
A pod compromise becomes a control-plane problem when workload identity turns execution into transitive authority. Kubernetes service-account tokens are not universal master keys, but permissive RBAC, workload federation, cloud IAM, and reachable credentials can connect one application incident to cluster and cloud impact.
Approving an agent tool once is not the same as trusting it forever. When mutable MCP descriptions and schemas influence the model’s decisions, routine metadata updates can alter the authority an enterprise thought it had approved..
A malicious dependency is no longer only an artifact problem. Attackers can distribute behavior across packages, build stages, and mutable infrastructure while hostile repository context pressures AI-assisted workflows elsewhere in the approval path.