[FORECAST] Ransomware Is Moving the Helpdesk Off the Server
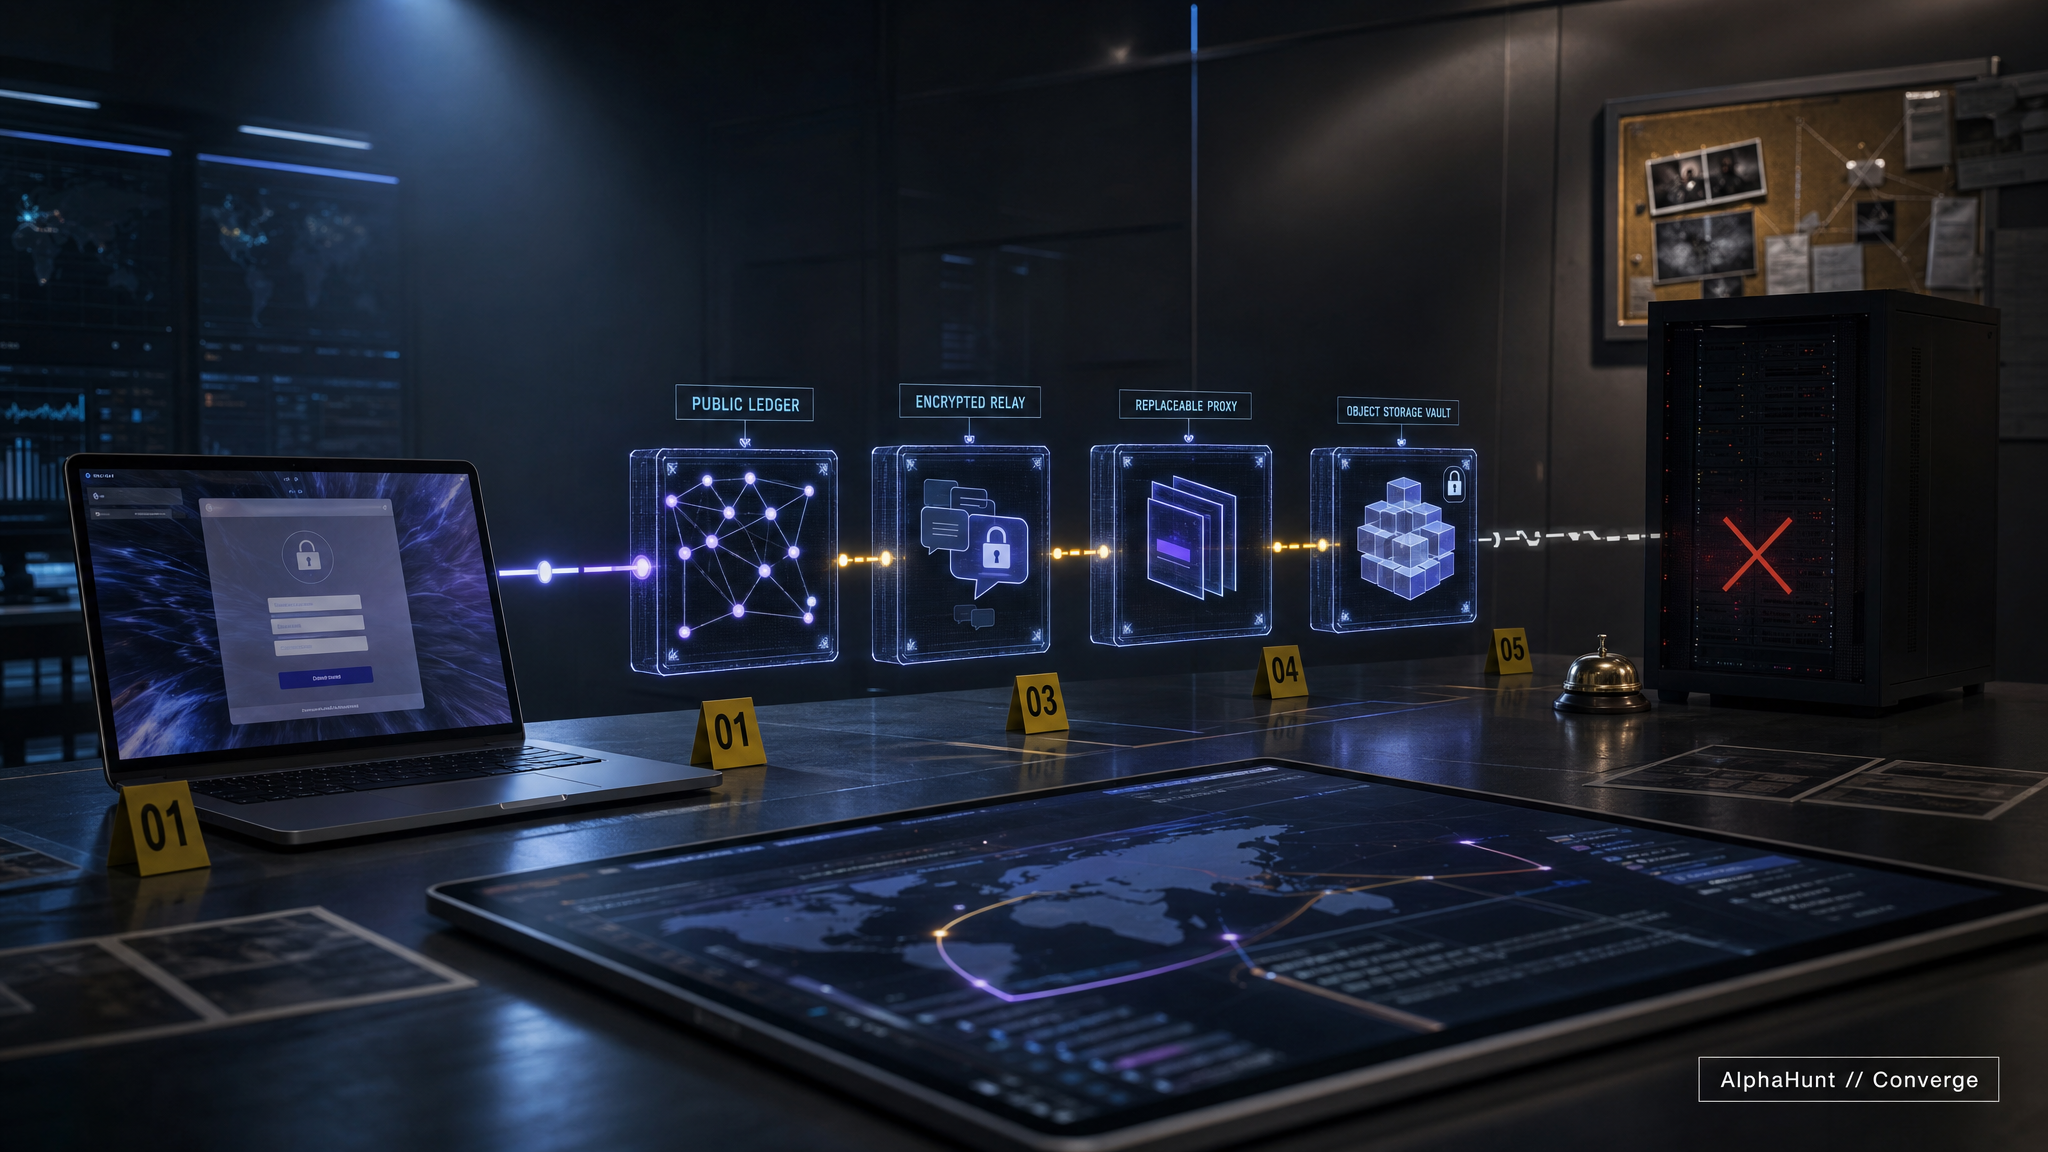
“Blockchain ransomware” is the easy headline. The harder operational problem is extortion workflow survivability.
“Blockchain ransomware” is the easy headline. The harder operational problem is extortion workflow survivability.
AlphaHunt examines how ransomware-as-a-service turns familiar enterprise weaknesses into repeatable extortion inputs—and why recovery maturity changes the attacker’s continuation game only after access. The full analysis separates observed behavior from assessed motive, maps operator, affiliate, broker, victim, government, and insurer incentives, and gives defenders a practical way to pressure the edge-to-recovery path before encryption.
Industrial incident reporting often gives analysts the loudest facts first: ransomware branding, a production halt, and a statement that no physical impact was confirmed. Those facts matter, but they do not answer the harder question—what did the adversary learn about the process?
We put a 30% chance on two public FCEB cases proving post-deadline edge exploitation by year-end.
A malicious package can be removed. A credential harvested from the build path can keep creating risk long after the incident looks closed. That is why “cleanup” and “containment” are not the same word, even if a dashboard would very much like them to be.
Legacy access paths have a nasty habit of surviving architecture updates, migration plans, and confident diagrams. The Check Point IKEv1 case is useful because it points at a larger defender problem: attackers are not only chasing fresh bugs. They are testing whether yesterday’s compatibility debt still works today.
We’re revising the Akira hospital disruption forecast down to 2%. The risk is real, but the question is narrower than it looks.