[GAME THEORY] Who can keep an incident open after the vulnerable server is patched?
Integrity Tech’s scanning-to-collection model puts the decision on attack-path ownership, not another attribution desk.
Integrity Tech’s scanning-to-collection model puts the decision on attack-path ownership, not another attribution desk.
Integrity Tech's capability mix changes the investment question: which routes to mail and identity remain after remediation?
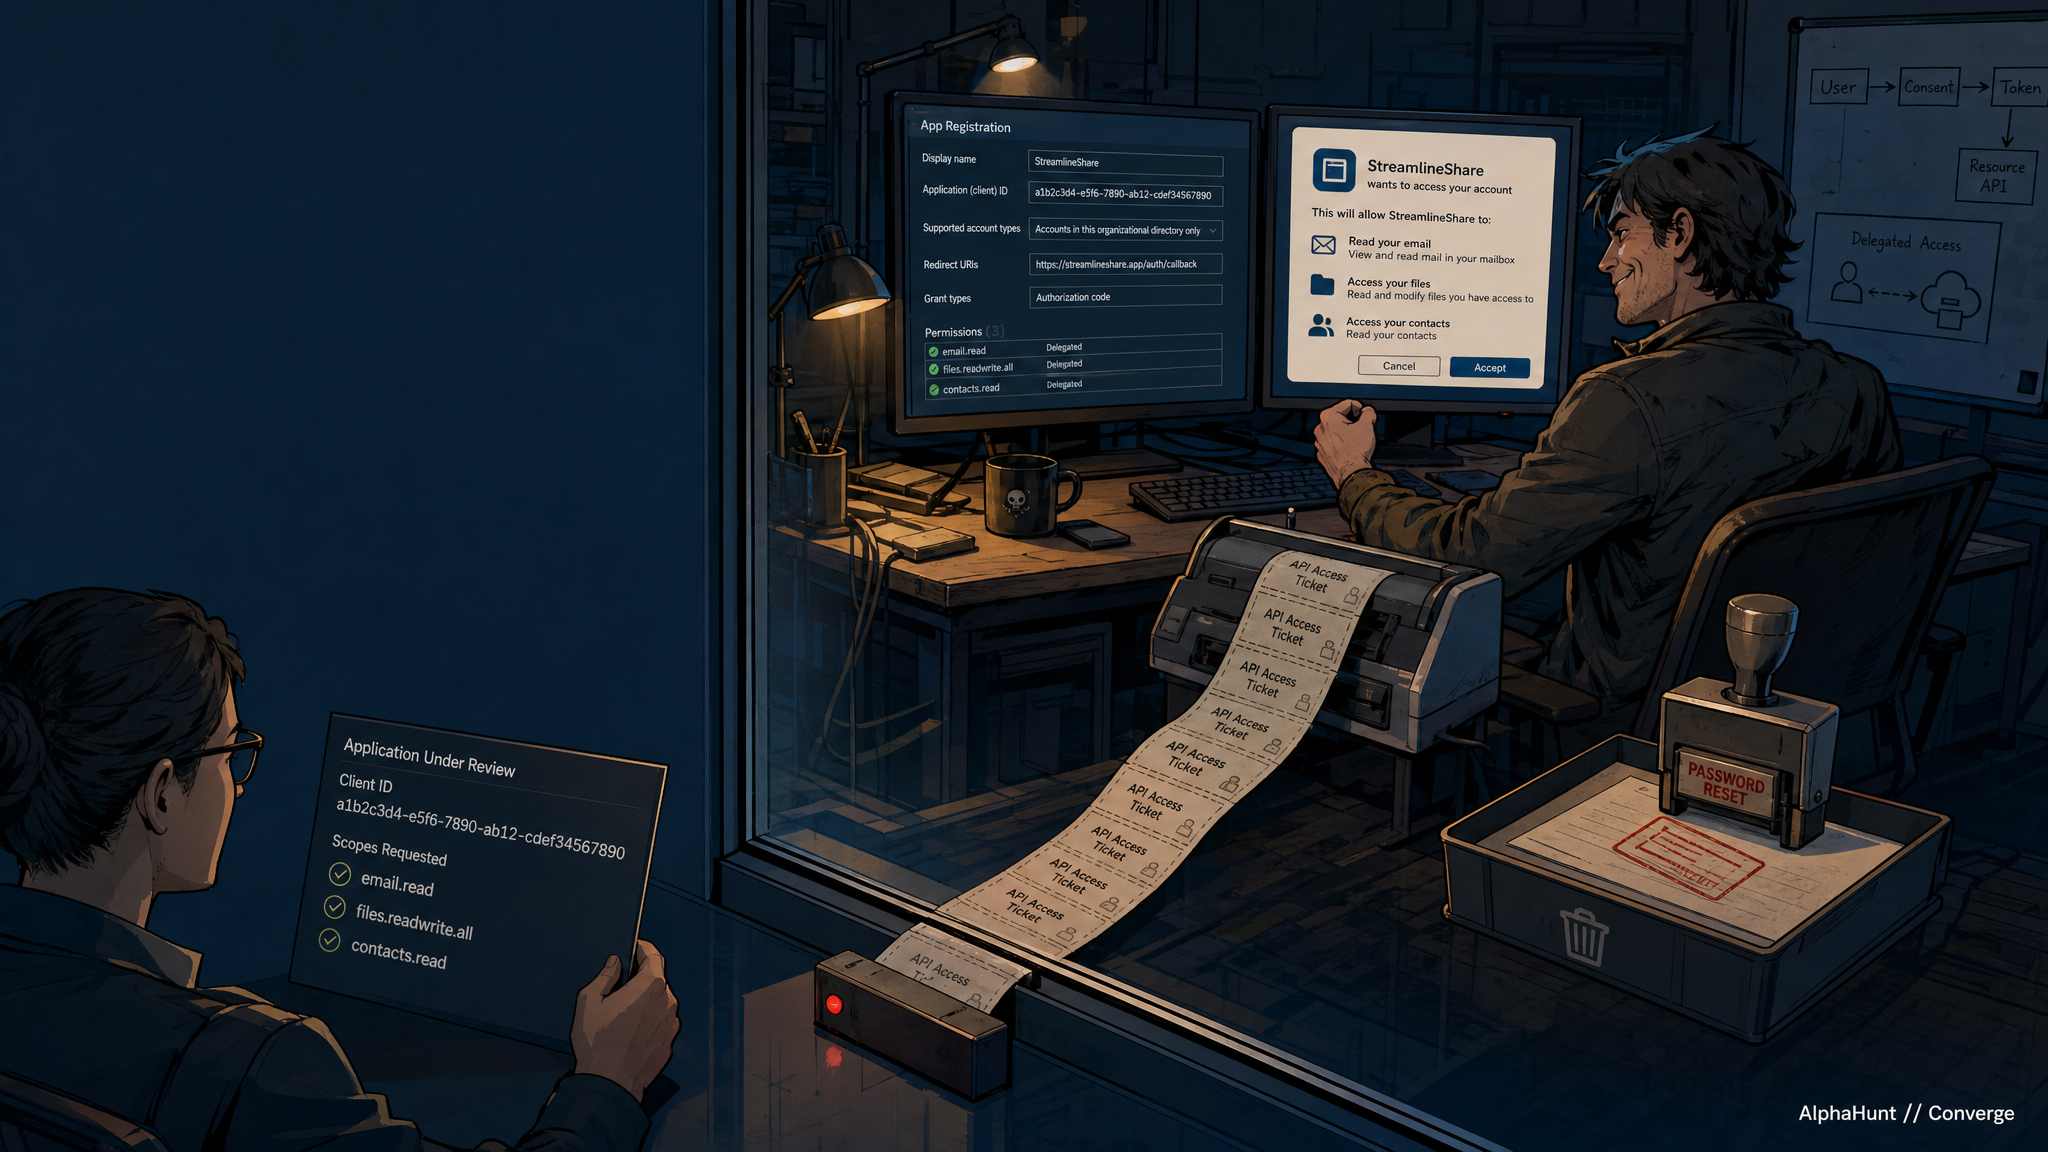
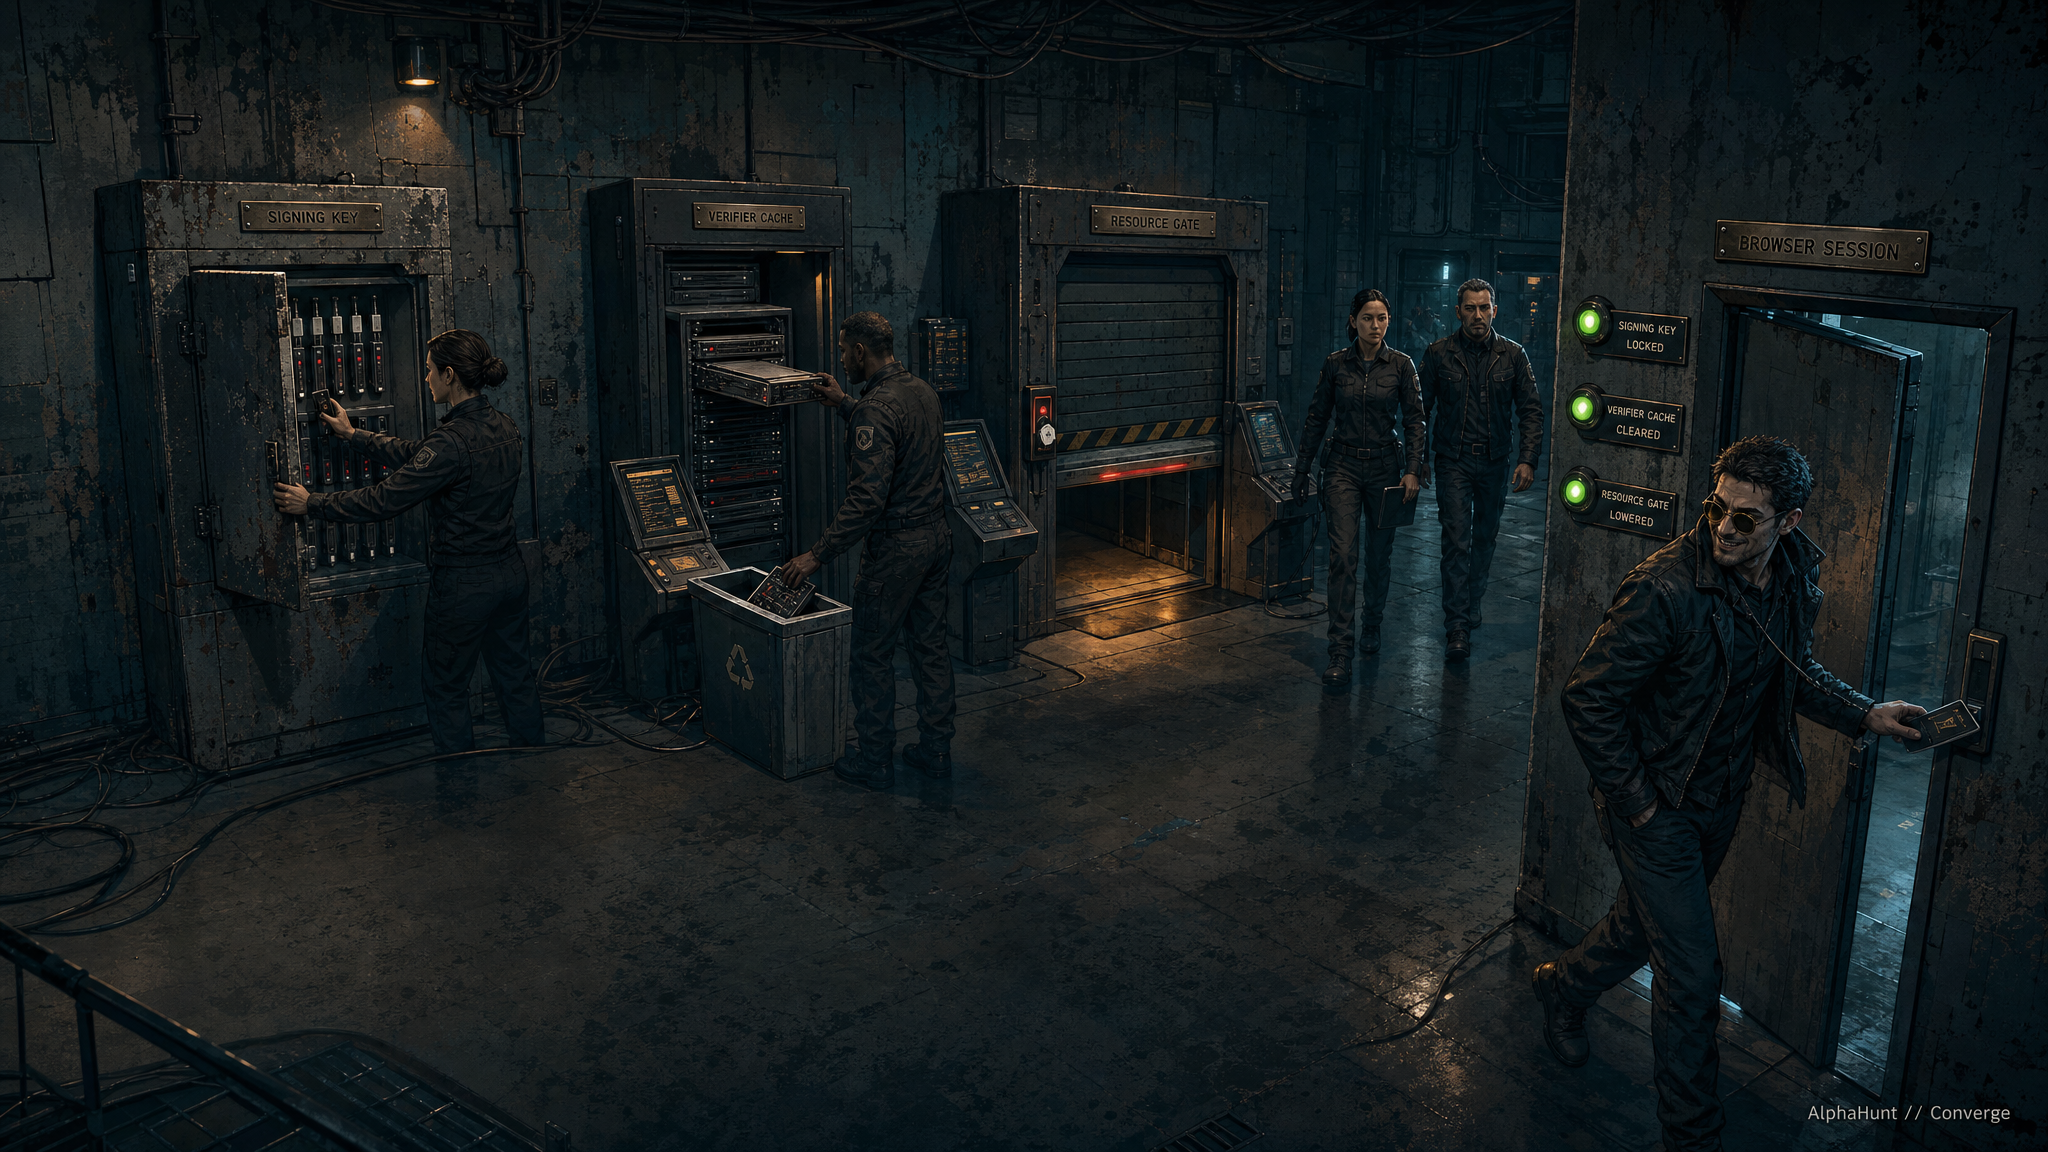
The attacker wants a durable app grant, not a password. Decide who can consent, what needs review, and how you prove revocation.
NetScaler shows why version compliance, compromise assessment, and restored trust are three different jobs.
A new joint advisory links recruiter malware and some DPRK IT workers. Here is where to join hiring, access, and payment decisions.
A 58% disclosure forecast—and the ownership test that matters before the next campaign is named.
Map the trust chain, measure the containment gap, and test the three token failures most likely to survive a routine response.