[DEEP RESEARCH] Containment Ends at the Last Denial, Not the First Click
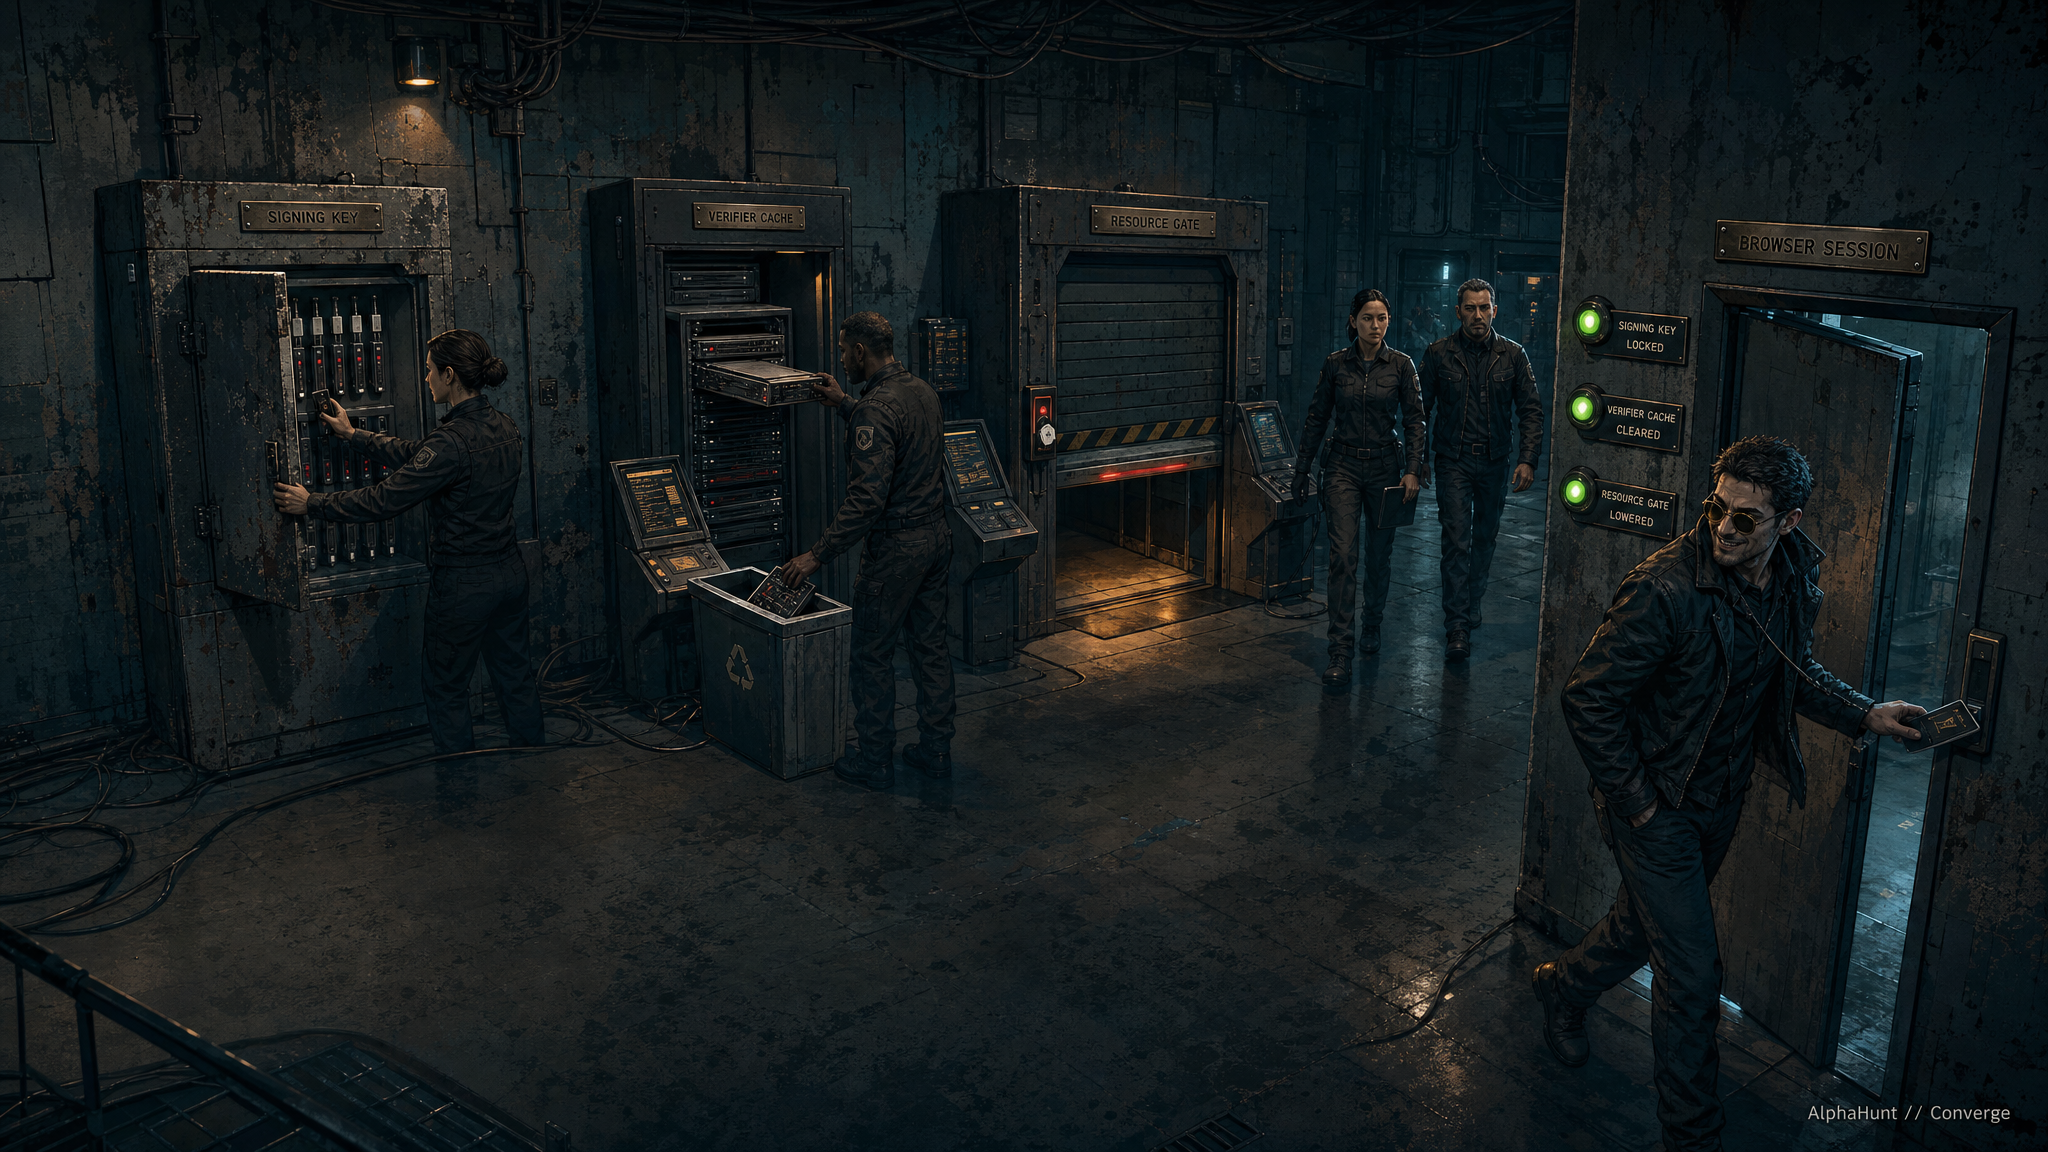
Map the trust chain, measure the containment gap, and test the three token failures most likely to survive a routine response.
Map the trust chain, measure the containment gap, and test the three token failures most likely to survive a routine response.
Two incidents appear to clear the bar. Govern AI credentials by replay value and blast radius before access becomes impact.
The next software supply-chain breach may not begin with malicious code. It may begin with a legitimate connector carrying a stolen OAuth token and the permissions customers already granted it
Device-code phishing turns a legitimate login flow into rented access. The durable defense is to shrink who can use it.
The user may start the incident. OAuth apps, tokens, and integrations can turn it into quiet, scalable data theft.
AI gateways are starting to concentrate credentials, logs, routing, quotas, and policy. That makes them worth watching now.
“Secure by default” sounds great until it meets BYOD, VDI, federated SSO, and the help desk exception list from hell.
Device-bound sessions help.
Waiting for every SaaS vendor to flip the default is not a strategy.