[GAME THEORY] Who actually owns revocation when a user approves a malicious OAuth app?
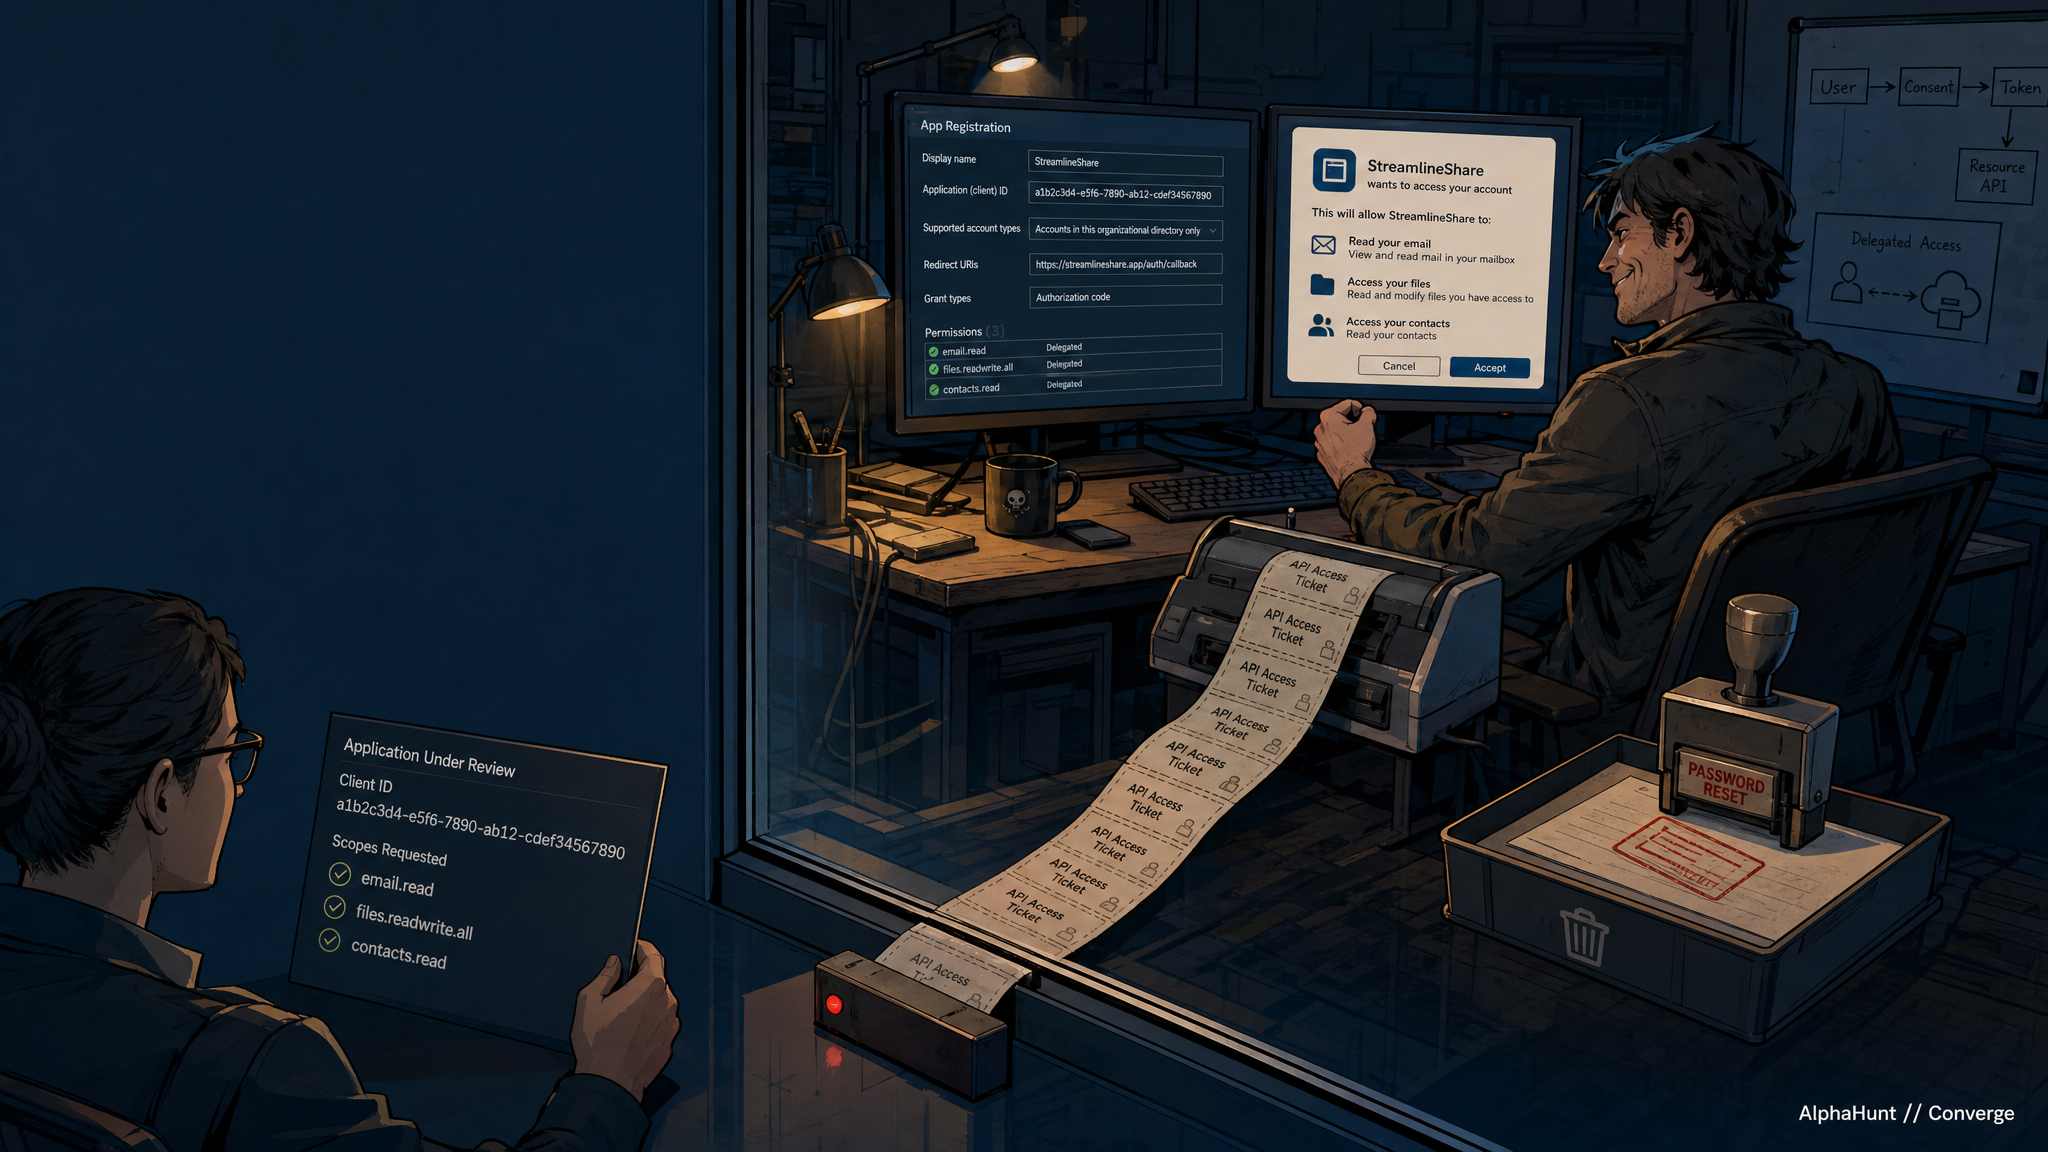
The attacker wants a durable app grant, not a password. Decide who can consent, what needs review, and how you prove revocation.
The attacker wants a durable app grant, not a password. Decide who can consent, what needs review, and how you prove revocation.
Vishing works because urgency can become SaaS authority. Break the trust transaction without breaking support.
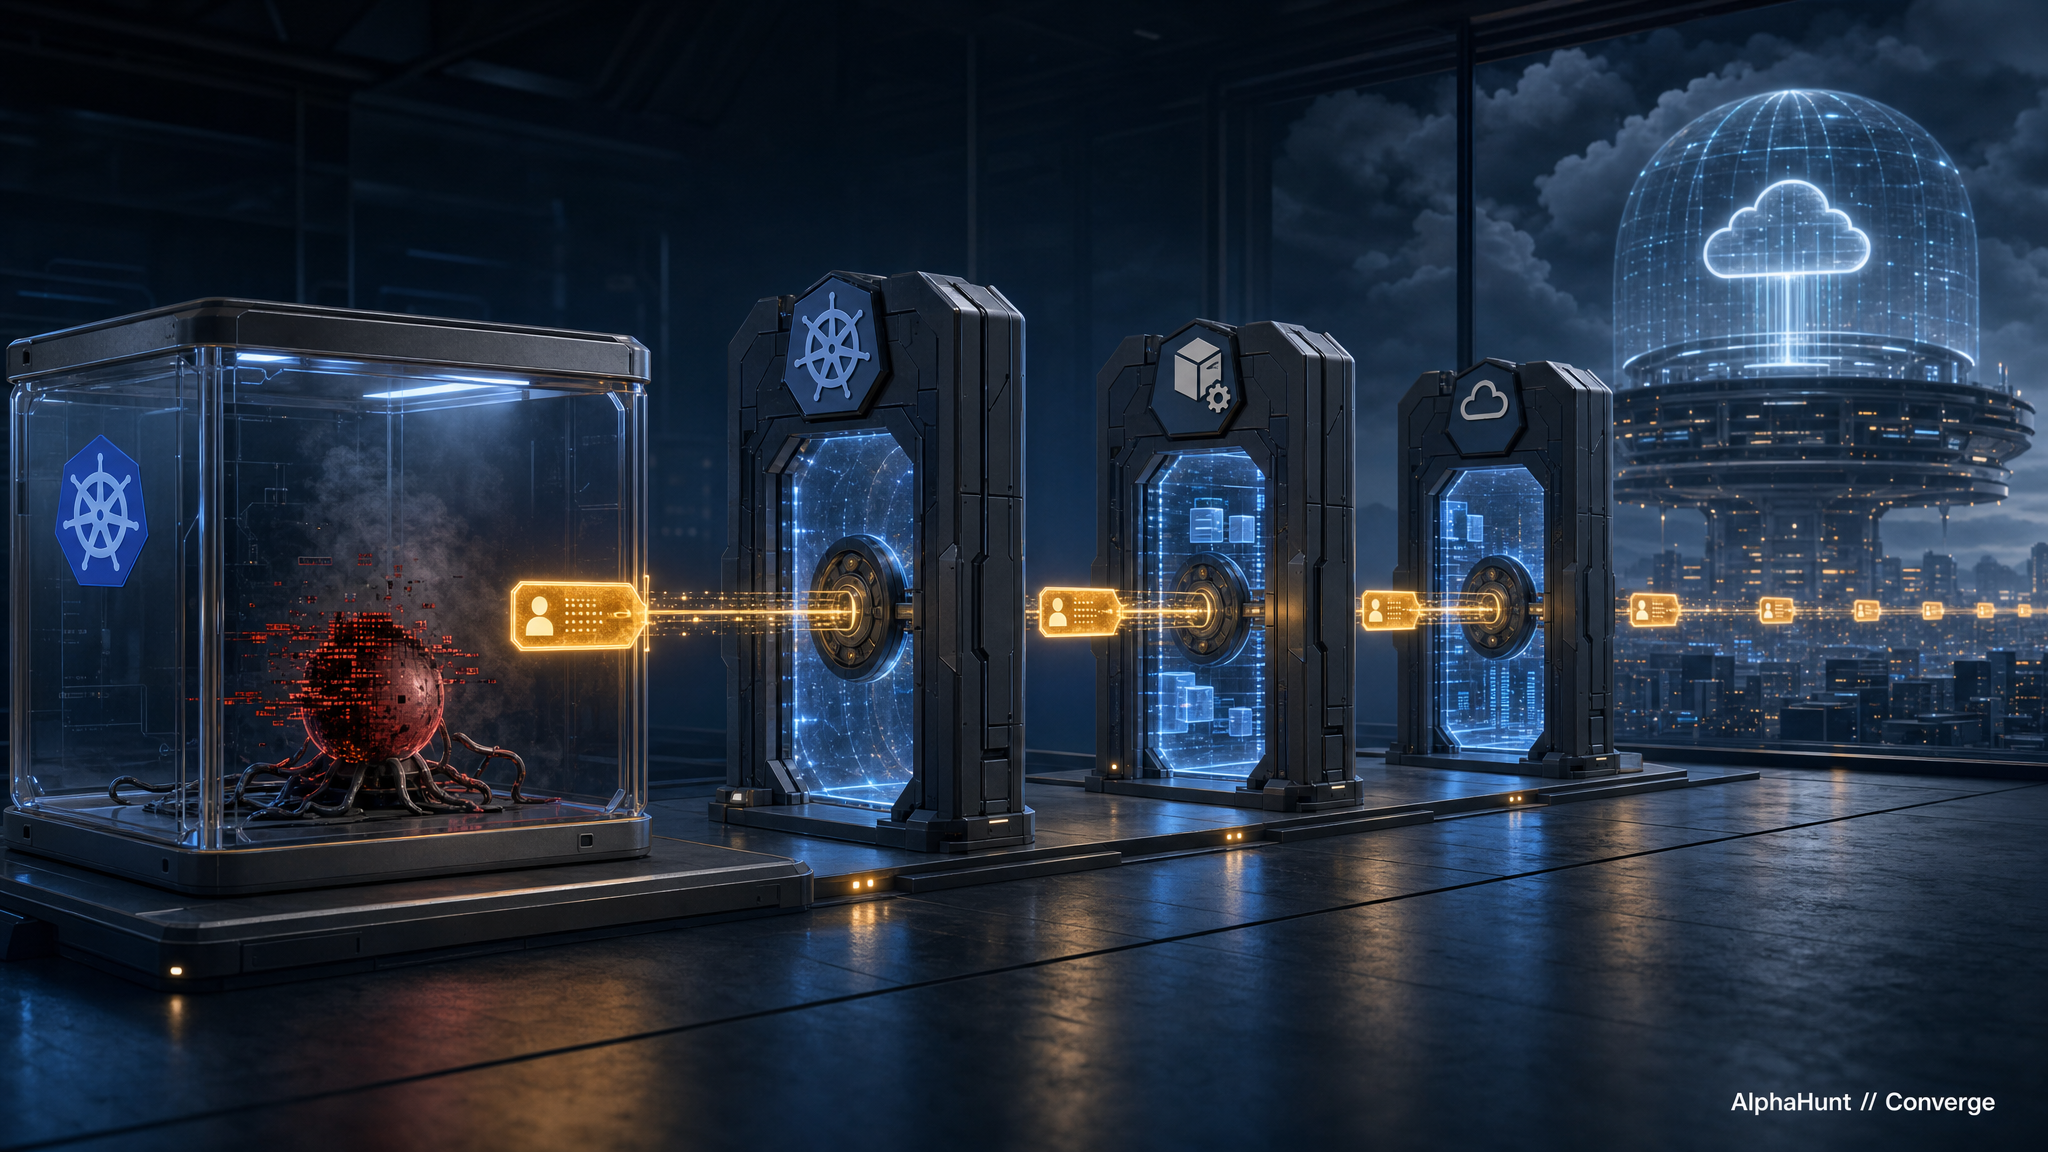
A pod compromise becomes a control-plane problem when workload identity turns execution into transitive authority. Kubernetes service-account tokens are not universal master keys, but permissive RBAC, workload federation, cloud IAM, and reachable credentials can connect one application incident to cluster and cloud impact.
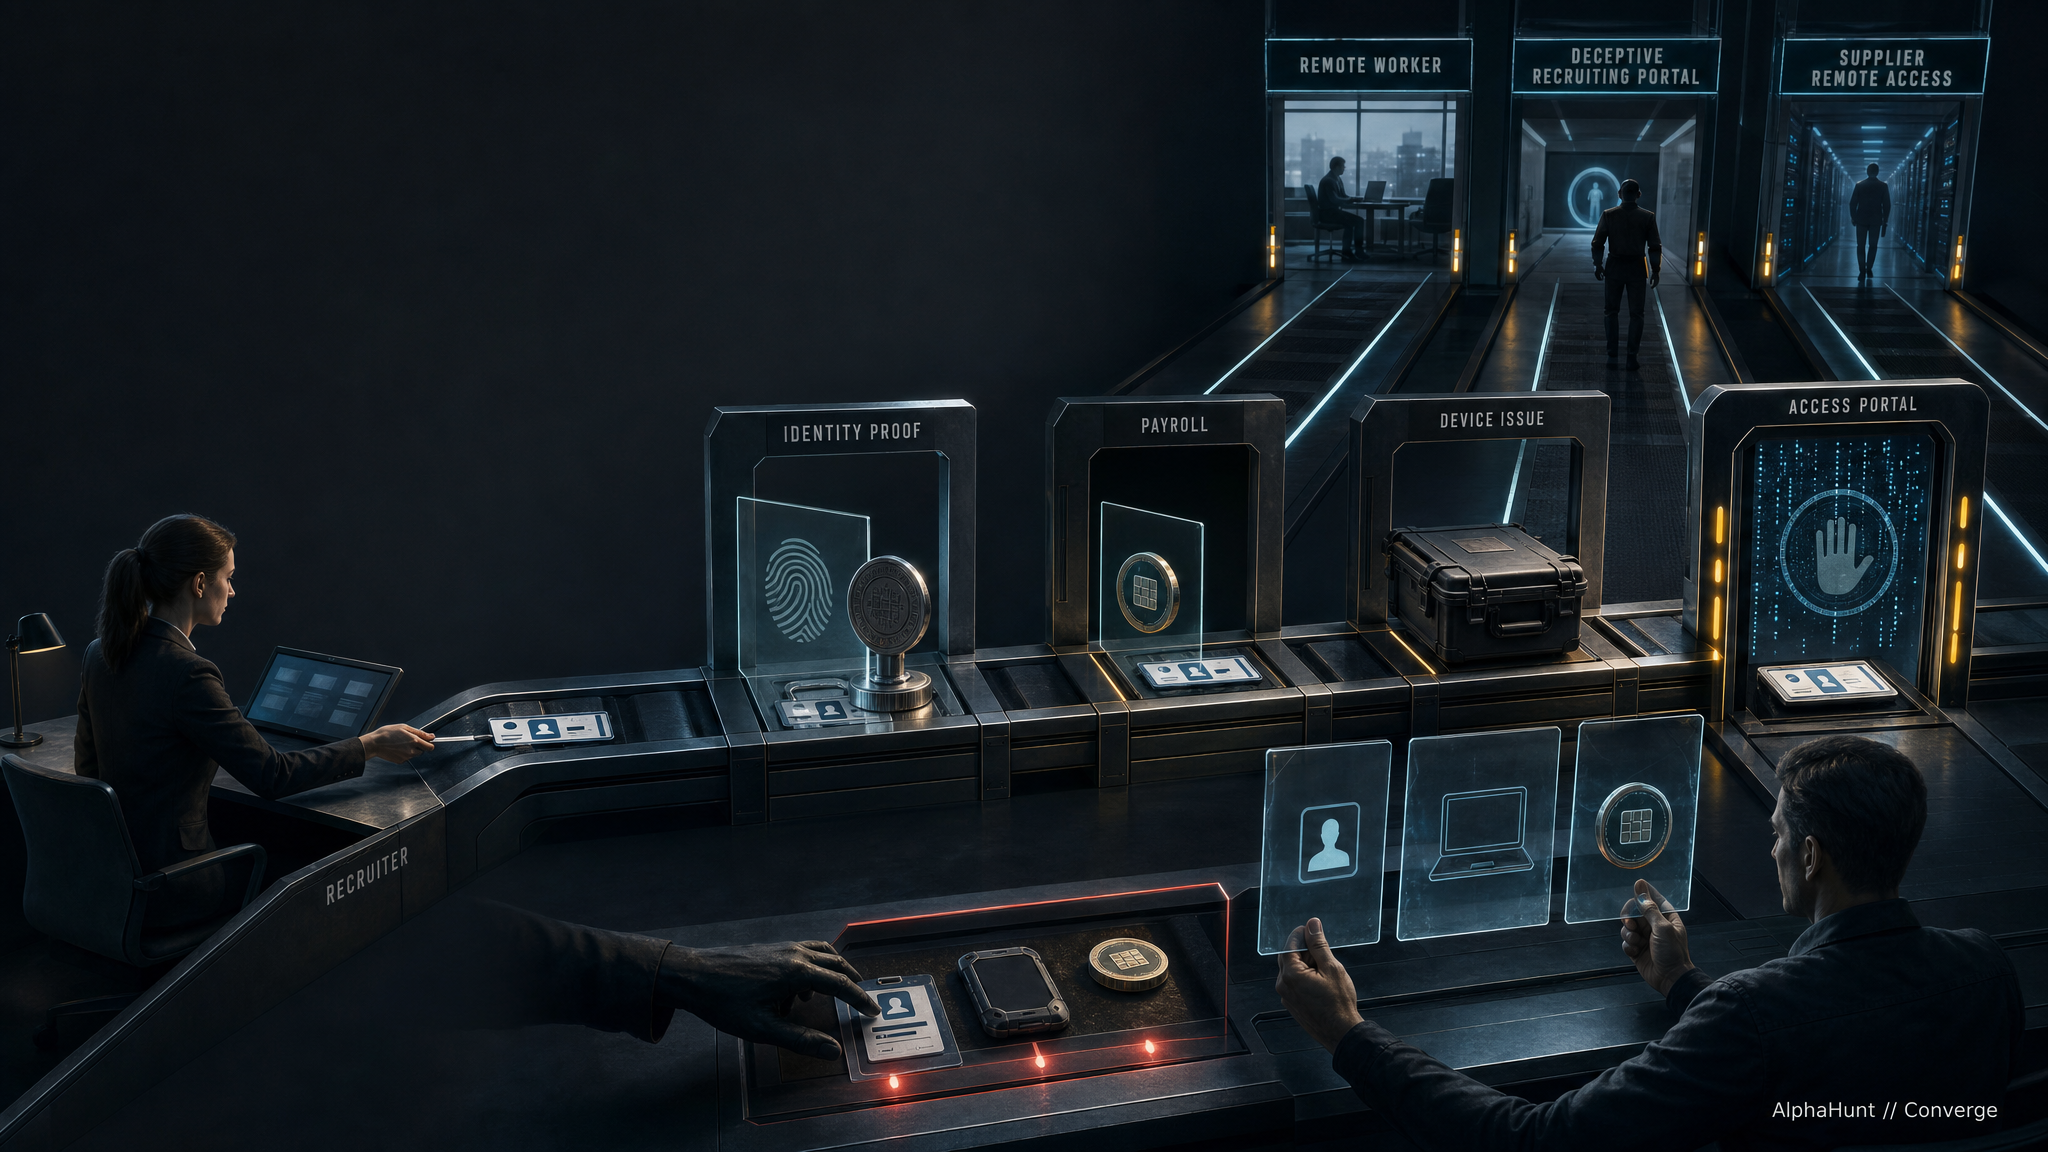
Defense-industrial access can form before a conventional security workflow has a stable employee, device, or account to monitor. DPRK IT-worker schemes, suspected Iran-nexus recruitment operations, and supplier compromise remain distinct threats, but they expose the same defensive problem: workforce and delegated authority are often created from evidence scattered across teams that do not routinely compare records.