[GAME THEORY] Who can keep an incident open after the vulnerable server is patched?
Integrity Tech’s scanning-to-collection model puts the decision on attack-path ownership, not another attribution desk.
Integrity Tech’s scanning-to-collection model puts the decision on attack-path ownership, not another attribution desk.
Integrity Tech's capability mix changes the investment question: which routes to mail and identity remain after remediation?
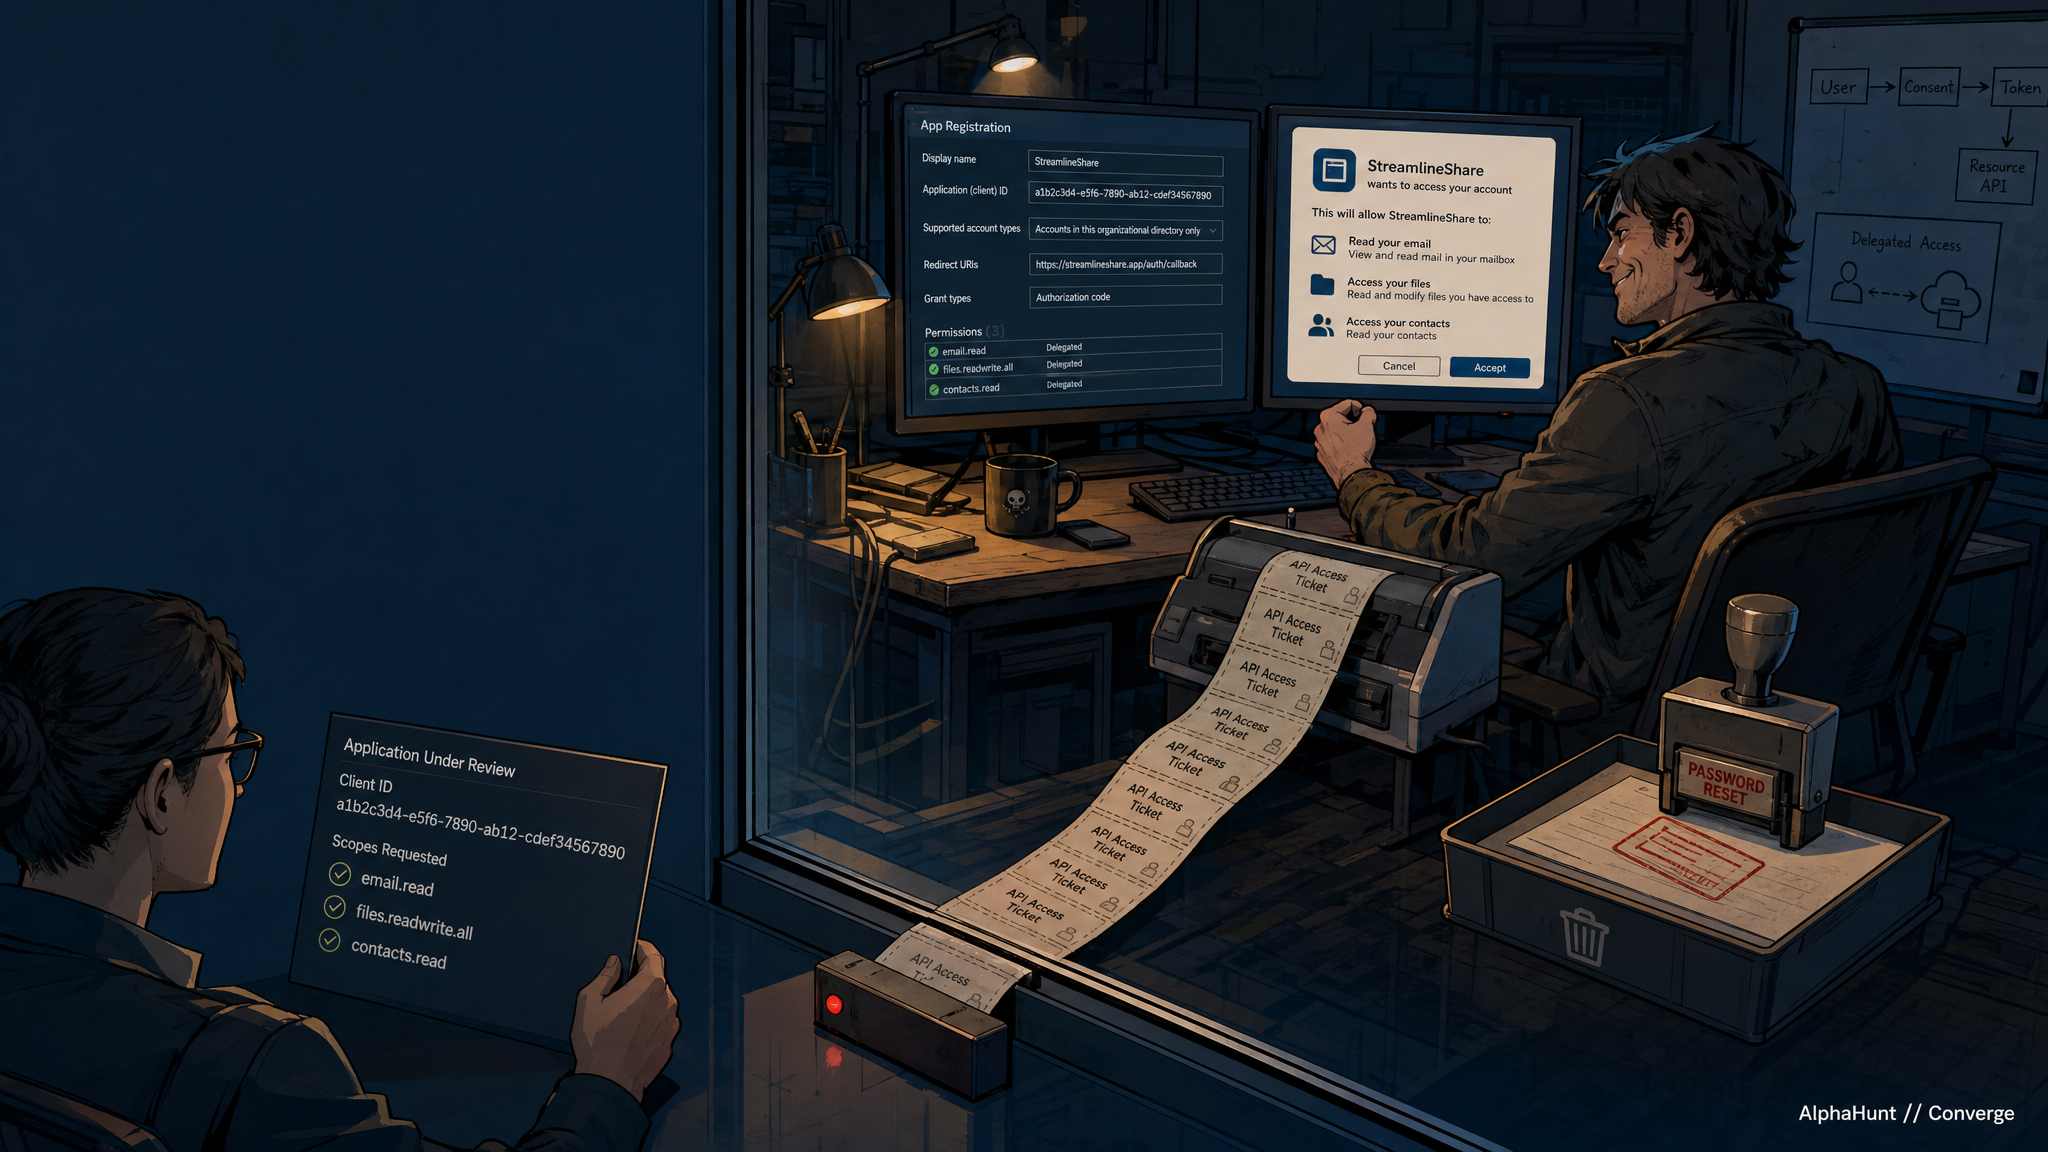
The attacker wants a durable app grant, not a password. Decide who can consent, what needs review, and how you prove revocation.
A new joint advisory links recruiter malware and some DPRK IT workers. Here is where to join hiring, access, and payment decisions.
The attacker needs sustained, useful output. Defenders can turn that dependency into friction across the access ecosystem.
Shared intrusion logistics can be a better chokepoint than one APT—if defenders can prove real control-plane dependence.
Vishing works because urgency can become SaaS authority. Break the trust transaction without breaking support.