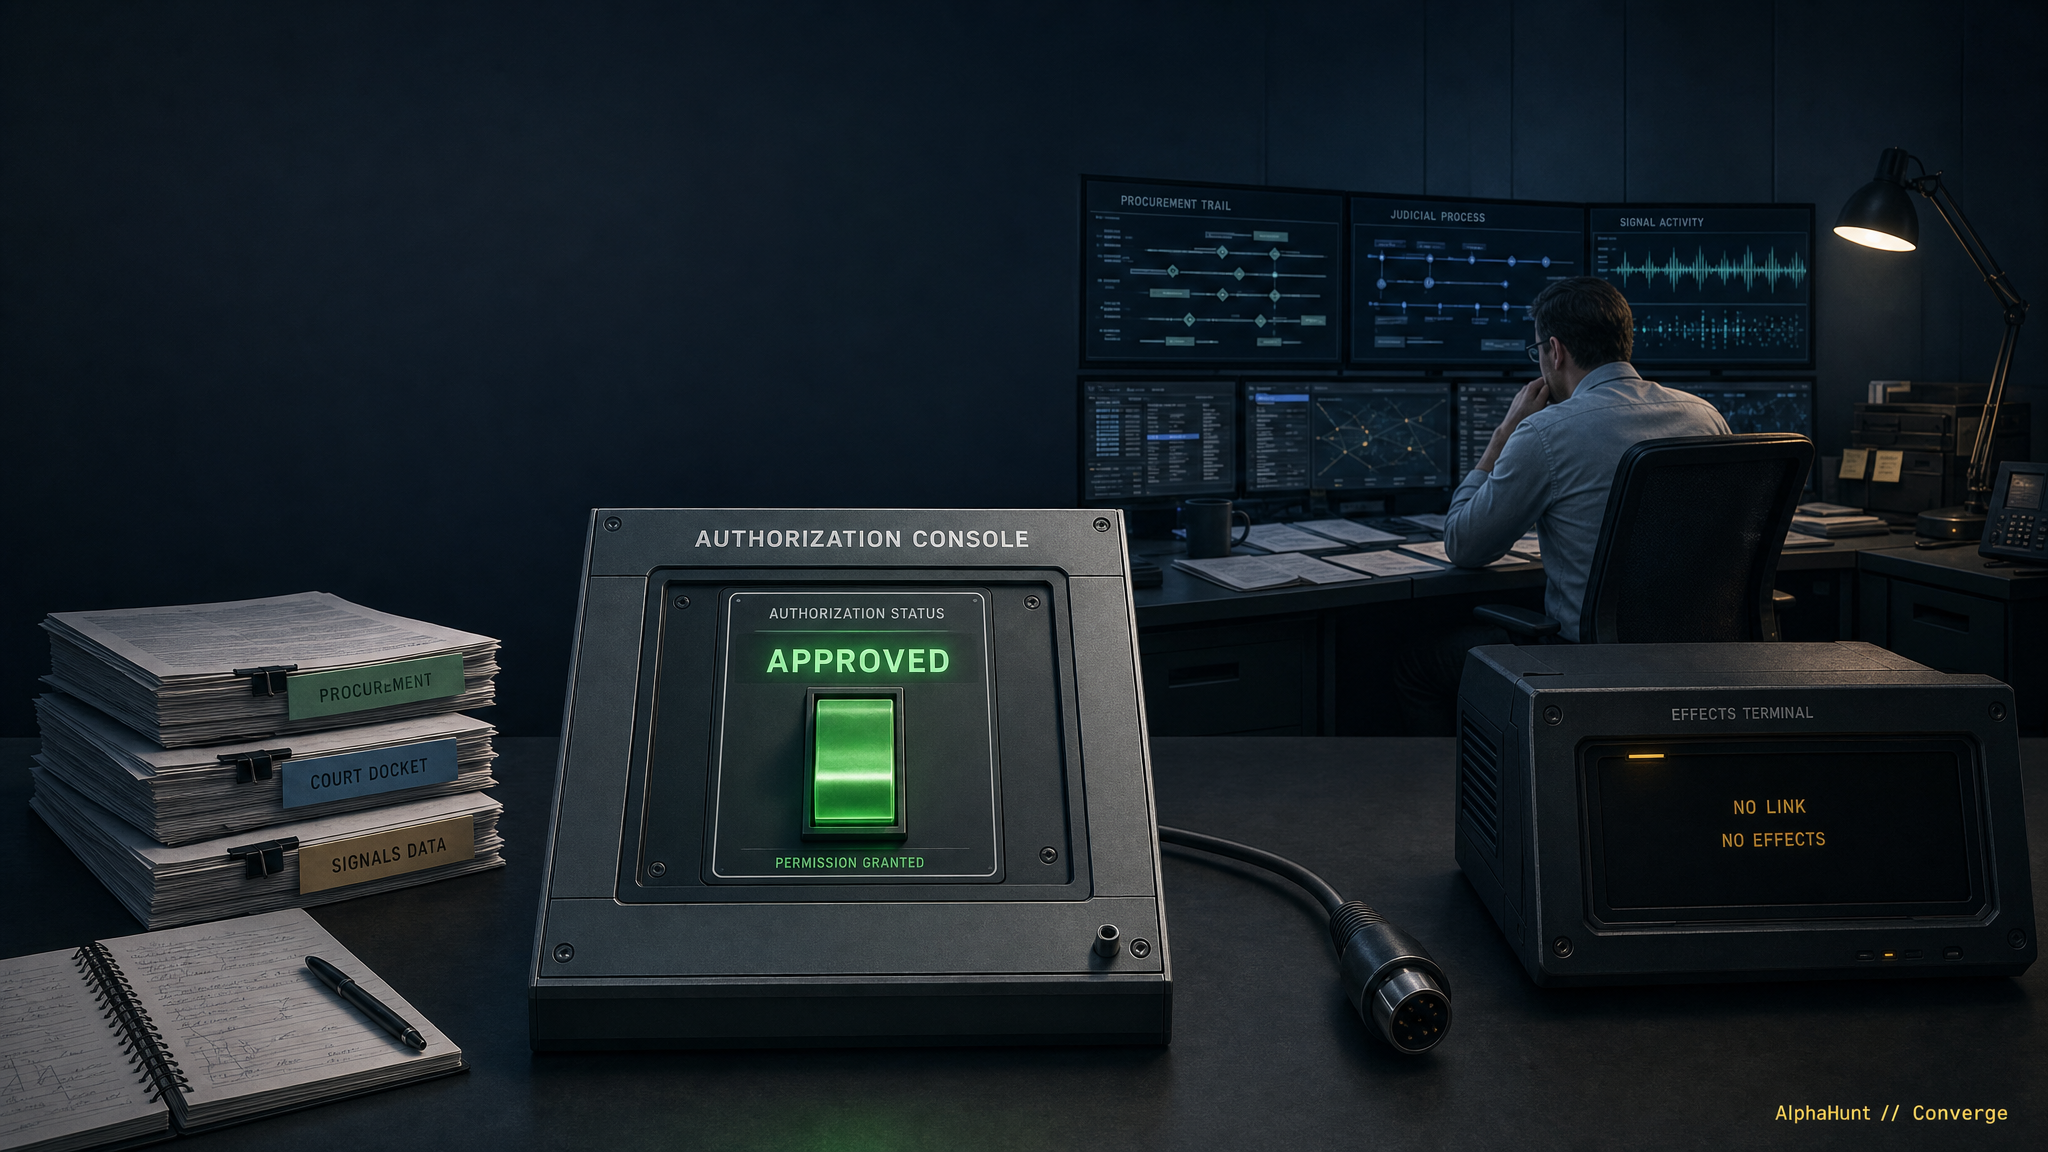
[FORECAST] Authorization Is Public; Execution May Stay Hidden
Our 45% forecast—and the public signals that would show private cyber effects have moved from authority to action.
Our 45% forecast—and the public signals that would show private cyber effects have moved from authority to action.
“Blockchain ransomware” is the easy headline. The harder operational problem is extortion workflow survivability.
The next software supply-chain breach may not begin with malicious code. It may begin with a legitimate connector carrying a stolen OAuth token and the permissions customers already granted it
We put a 30% chance on two public FCEB cases proving post-deadline edge exploitation by year-end.
A firewall, VPN, or secure-access gateway can hold much more than vulnerable code. It can mediate trusted sessions, store service-account credentials, expose configuration secrets, and connect external identities to internal systems. Once those artifacts leave the appliance, remediation becomes a trust-recovery problem—not only a software-maintenance task.
China-linked operators are turning compromised routers into relay logistics. The defender move is behavior over bad IPs.
A malicious package can be removed. A credential harvested from the build path can keep creating risk long after the incident looks closed. That is why “cleanup” and “containment” are not the same word, even if a dashboard would very much like them to be.