[FORECAST] Authorization Is Public; Execution May Stay Hidden
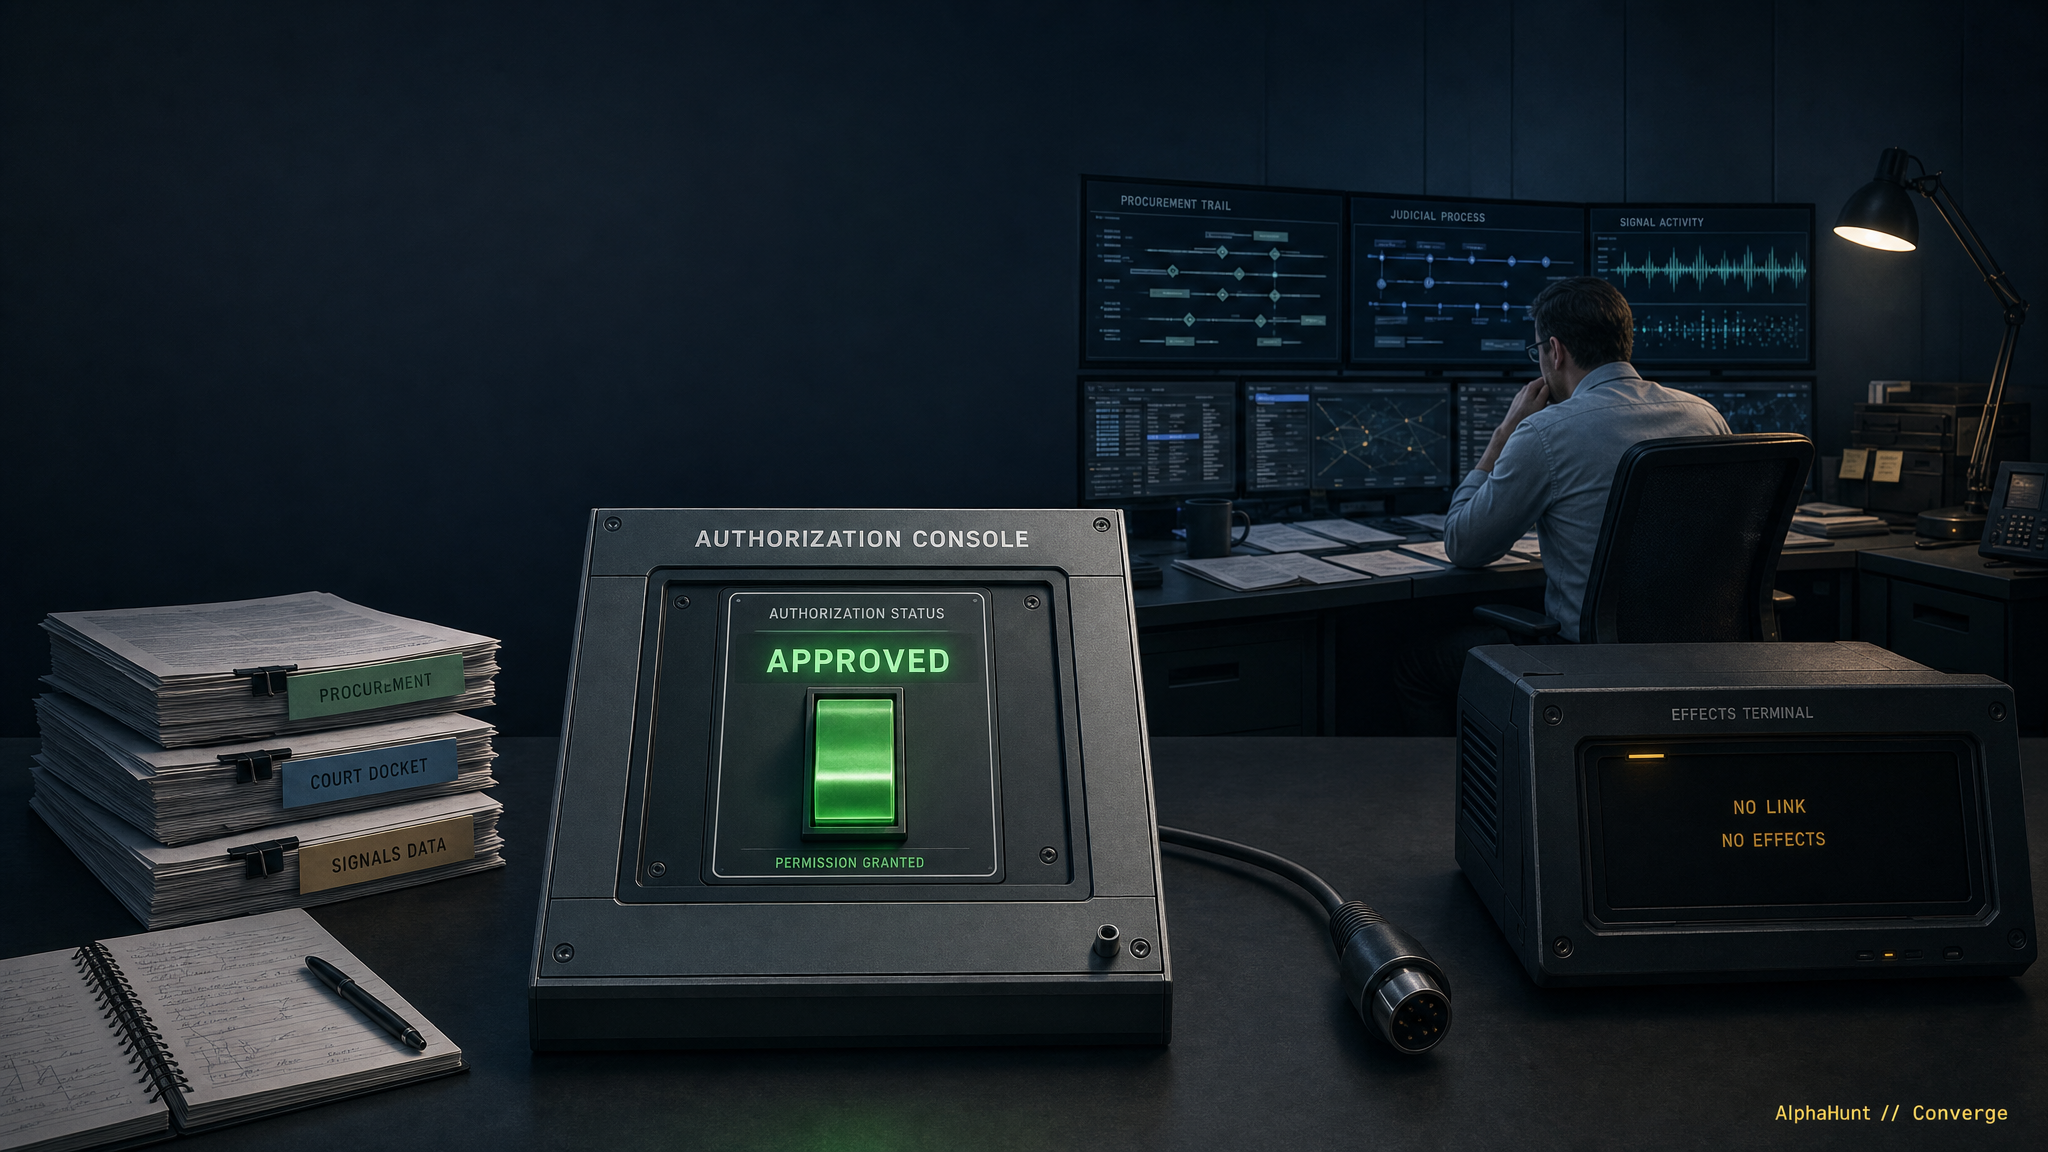
Our 45% forecast—and the public signals that would show private cyber effects have moved from authority to action.
Our 45% forecast—and the public signals that would show private cyber effects have moved from authority to action.
Vishing works because urgency can become SaaS authority. Break the trust transaction without breaking support.
AlphaHunt examines how ransomware-as-a-service turns familiar enterprise weaknesses into repeatable extortion inputs—and why recovery maturity changes the attacker’s continuation game only after access. The full analysis separates observed behavior from assessed motive, maps operator, affiliate, broker, victim, government, and insurer incentives, and gives defenders a practical way to pressure the edge-to-recovery path before encryption.
Defense-industrial access can form before a conventional security workflow has a stable employee, device, or account to monitor. DPRK IT-worker schemes, suspected Iran-nexus recruitment operations, and supplier compromise remain distinct threats, but they expose the same defensive problem: workforce and delegated authority are often created from evidence scattered across teams that do not routinely compare records.
Industrial incident reporting often gives analysts the loudest facts first: ransomware branding, a production halt, and a statement that no physical impact was confirmed. Those facts matter, but they do not answer the harder question—what did the adversary learn about the process?
Device-code phishing turns a legitimate login flow into rented access. The durable defense is to shrink who can use it.
The user may start the incident. OAuth apps, tokens, and integrations can turn it into quiet, scalable data theft.